Application and Data Vulnerabilities and Attacks
Introduced
Vocabulary
| English | Meaning |
|---|---|
| injection attack/ɪnˈdʒekʃn əˈtæk/ | An attack in which untrusted input is interpreted as instructions by a system, changing its intended operation. |
| data validation/ˈdeɪtə ˌvælɪˈdeɪʃn/ | The core defense; rate data risk by sensitivity. |
| SQL injection/ˌes kjuː ˈel ɪnˈdʒekʃn/ | An injection attack in which untrusted input is treated as SQL instructions and alters the intended database operation. |
| cross-site scripting/krɒs saɪt ˈskrɪptɪŋ/ | cross-site scripting |
| buffer overflow/ˈbʌfə ˌəʊvəˈfləʊ/ | buffer overflow |
| buffer/ˈbʌfə/ | A temporary area of memory used to hold data while it is transferred or processed. |
| directory traversal/daɪˈrektəri træˈvɜːsl/ | directory traversal |
Bad input is the danger
- When a program does not check input, an adversary slips in commands — an injection attack 注入攻击.
- Data validation 数据验证 (checking input meets rules) is the defense.
- Unencrypted files and over-broad admin rights add more risk.
SQL injection and XSS
- SQL injection SQL注入: SQL commands in an input field read or change a database.
- Cross-site scripting (XSS) 跨站脚本: injected script runs in another user's browser.
- Both come from trusting unchecked user input.
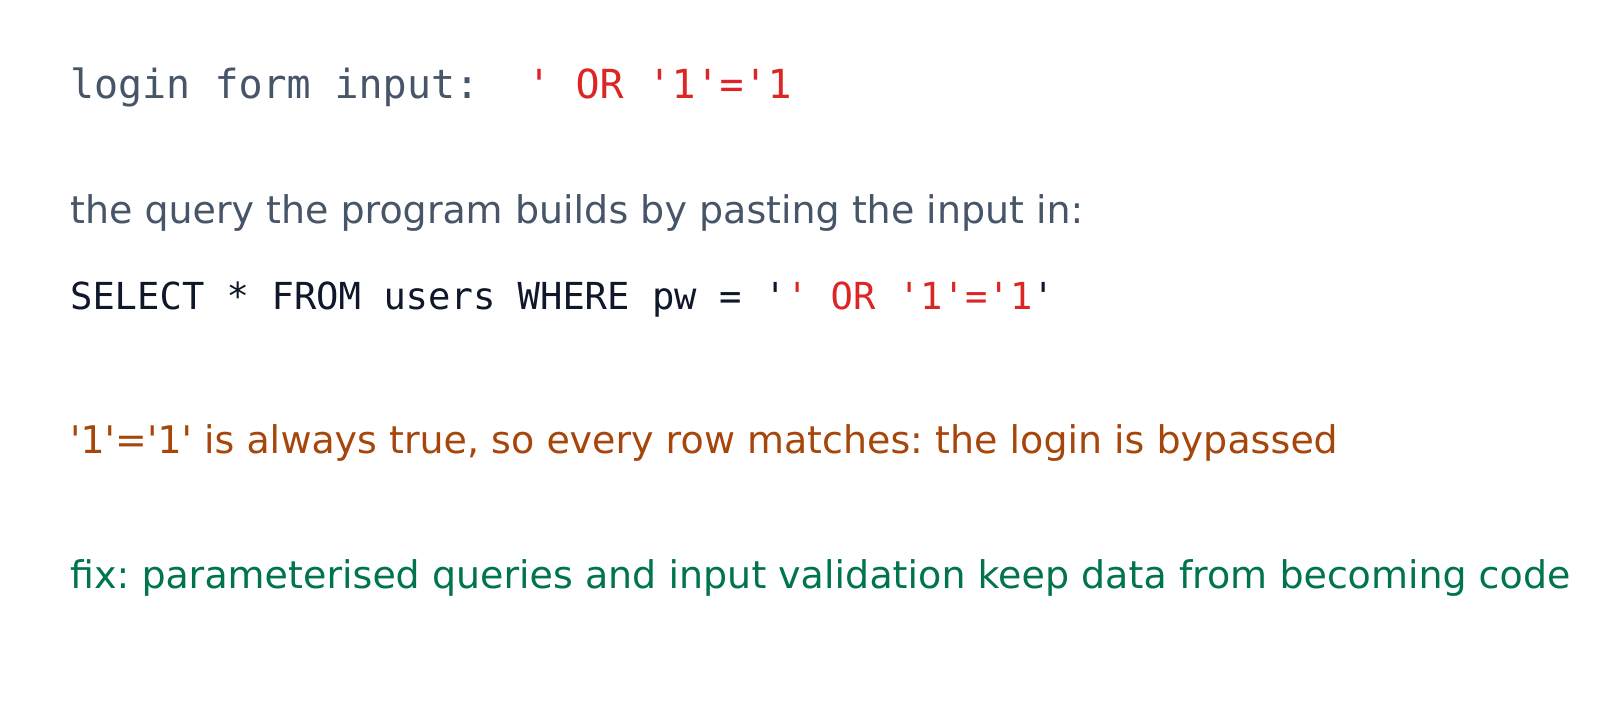
SQL injection: input pasted into a query changes the query itself
Explore
Identify the application attack from the evidence
SQL injection shows OR 1=1; XSS shows
Your subject
Loading subjects…
Exam dates
Pick one and the site follows you — notes, papers, videos and practice all open on it.