| Learning Objective | Essential Knowledge |
|---|---|
5.1.A |
|
5.1.B |
|
5.1.C |
|
Securing Applications and Data
AP Cybersecurity · Topic 5
5.1
Application and Data Vulnerabilities and Attacks
Syllabus
Source: College Board AP Course and Exam Description
Applications 应用程序 are the programs that run on computers, and data is what they process - both are prime targets. If files are stored unencrypted, anyone with access to the drive can read them. If a normal user is given administrative 管理性 privileges, an adversary who steals that account gains sweeping power.
The biggest application danger is bad user input. When a program does not check what a user types, an adversary can slip in commands - an injection attack 注入攻击. Data validation 数据验证 (checking input meets expected rules) is the defense. Key attacks:
- SQL injection SQL注入 - inserting SQL commands into an input field to read or change a database.
- Cross-site scripting (XSS) 跨站脚本 - injecting malicious script into a website that runs in another user's browser.
What a SQL injection actually looks like
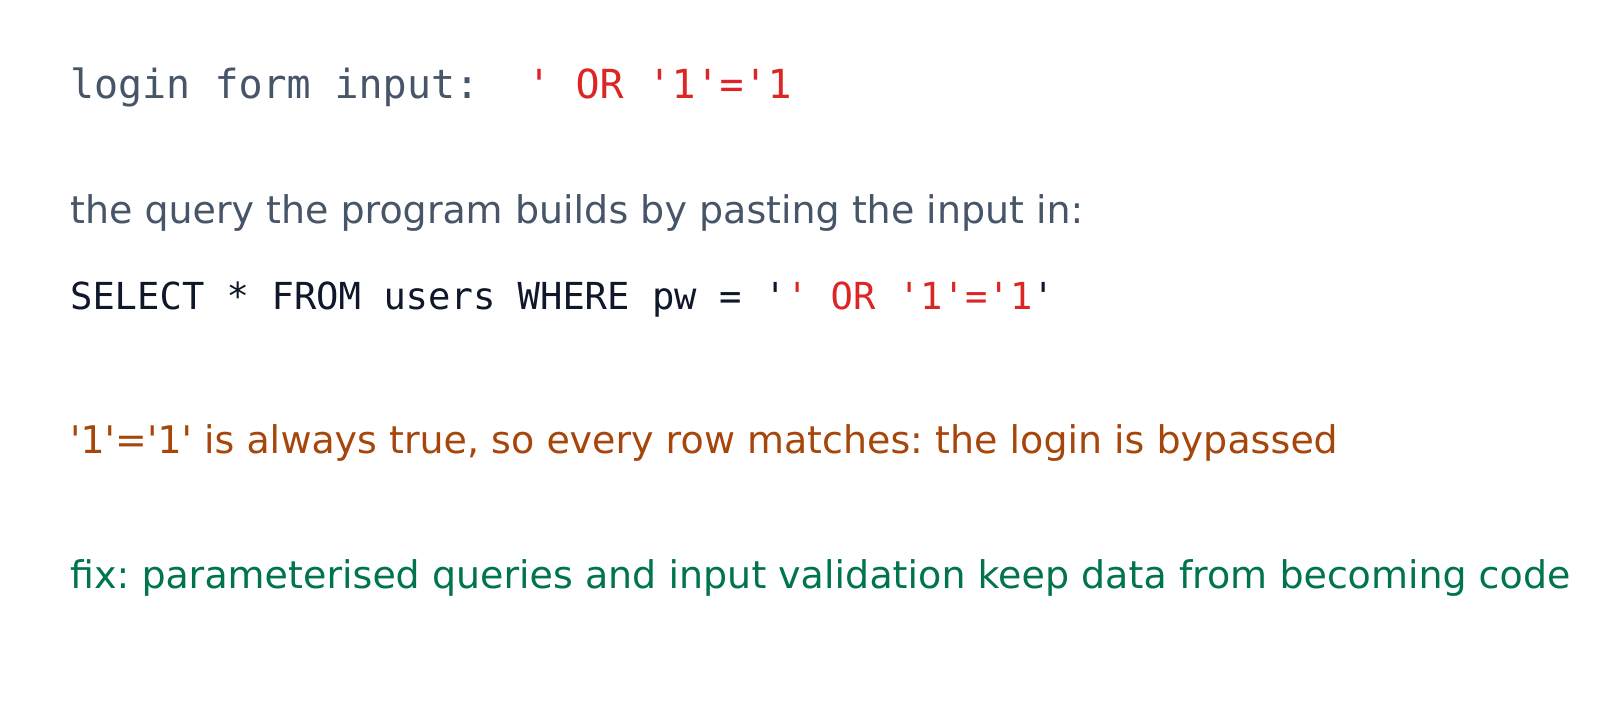
SQL is a language for querying a database, and its control words are conventionally written in capital letters (SQL itself ignores their case, so select works too) — SELECT, FROM, WHERE, IN, OR, AND. A login form usually builds a query by pasting what you typed into one:
SELECT * FROM users WHERE name = 'alice' AND password = 'secret'
An attacker types SQL into the field instead of a name. Two tricks do most of the damage:
- A condition that is always true. In the password field of the unsafe query shown, entering
' OR '1'='1changes its logic to(name = 'alice' AND password = '') OR '1'='1', which is true for every row. The same text in the name field does not automatically bypass the remaining password check. - A double dash, which begins a comment in SQL. Entering
admin' --ends the name string and comments out the whole rest of the line, including the password check, so the query becomes… WHERE name = 'admin'and the attacker is logged in as the administrator without a password.
The defence is not to filter for the word SELECT. It is to stop the input being treated as code at all: use parameterised queries 参数化查询 (also called prepared statements), where the database is given the query and the values separately and never mixes them, and add input validation to reject characters the field has no reason to contain.
- Buffer overflow 缓冲区溢出 - sending more data than a memory buffer 缓冲区 can hold, so it overflows into nearby memory and may run the adversary's code.
- Directory traversal 目录遍历 - using
../sequences in a URL to reach files outside the intended folder, such as/etc/passwd.
Rate data risk using both likelihood and impact. Sensitivity, exposure, access controls, encryption and credible threats matter; low-value data or a short key alone does not determine a fixed risk rating.
Vocabulary
Train
| English |
|---|
| Applications/ˌæplɪˈkeɪʃnz/ |
| administrative/ədˈmɪnɪstrətɪv/ |
| injection attack/ɪnˈdʒekʃn əˈtæk/ |
| Data validation/ˈdeɪtə ˌvælɪˈdeɪʃn/ |
| Cross-site scripting (XSS)/krɒs saɪt ˈskrɪptɪŋ/ |
| parameterised queries/ˌpærəˈmetəraɪzd ˈkwɪərɪz/ |
| Buffer overflow/ˈbʌfə ˌəʊvəˈfləʊ/ |
| buffer/ˈbʌfə/ |
| Directory traversal/daɪˈrektəri træˈvɜːsl/ |
| SQL injection/ˌes kjuː ˈel ɪnˈdʒekʃn/ |
5.2
Protecting Applications and Data: Managerial Controls and Access Controls
Syllabus
| Learning Objective | Essential Knowledge |
|---|---|
5.2.A |
|
5.2.B |
|
5.2.C |
|
5.2.D |
|
Source: College Board AP Course and Exam Description
Data is classified by its state - at rest 静态数据 (stored on a drive), in transit 传输中数据 (moving between devices), and in use 使用中数据 (being processed). Data at rest and in transit can be encrypted so a thief cannot read it; conventional processing normally decrypts data in use, so access controls and protection of memory and execution are also needed.
Some data types are regulated 受监管 - the law dictates how they must be stored, transmitted and handled - so an organisation must achieve compliance 合规 by matching its controls to the rules. The course pairs these data types with example U.S. legal frameworks or industry standards. Their scope matters; these are not universal one-to-one rules:
| Data type | What it is | Example framework and scope |
|---|---|---|
| personally identifiable information (PII) 个人身份信息 | information identifying or linked to a person | Privacy Act: U.S. federal-agency records; COPPA: covered online collection from children under 13 |
| protected health information (PHI) 受保护健康信息 | identifiable health information in covered contexts | HIPAA: covered entities and business associates, with defined scope and exclusions |
| payment card information (PCI) 支付卡信息 | payment-card account and authentication data | PCI DSS: an industry security standard for relevant card-data environments |
An organisation that collects regulated data must label it and hold policies that keep its storage, transmission and handling compliant - the higher the sensitivity, the higher the required degree of security.
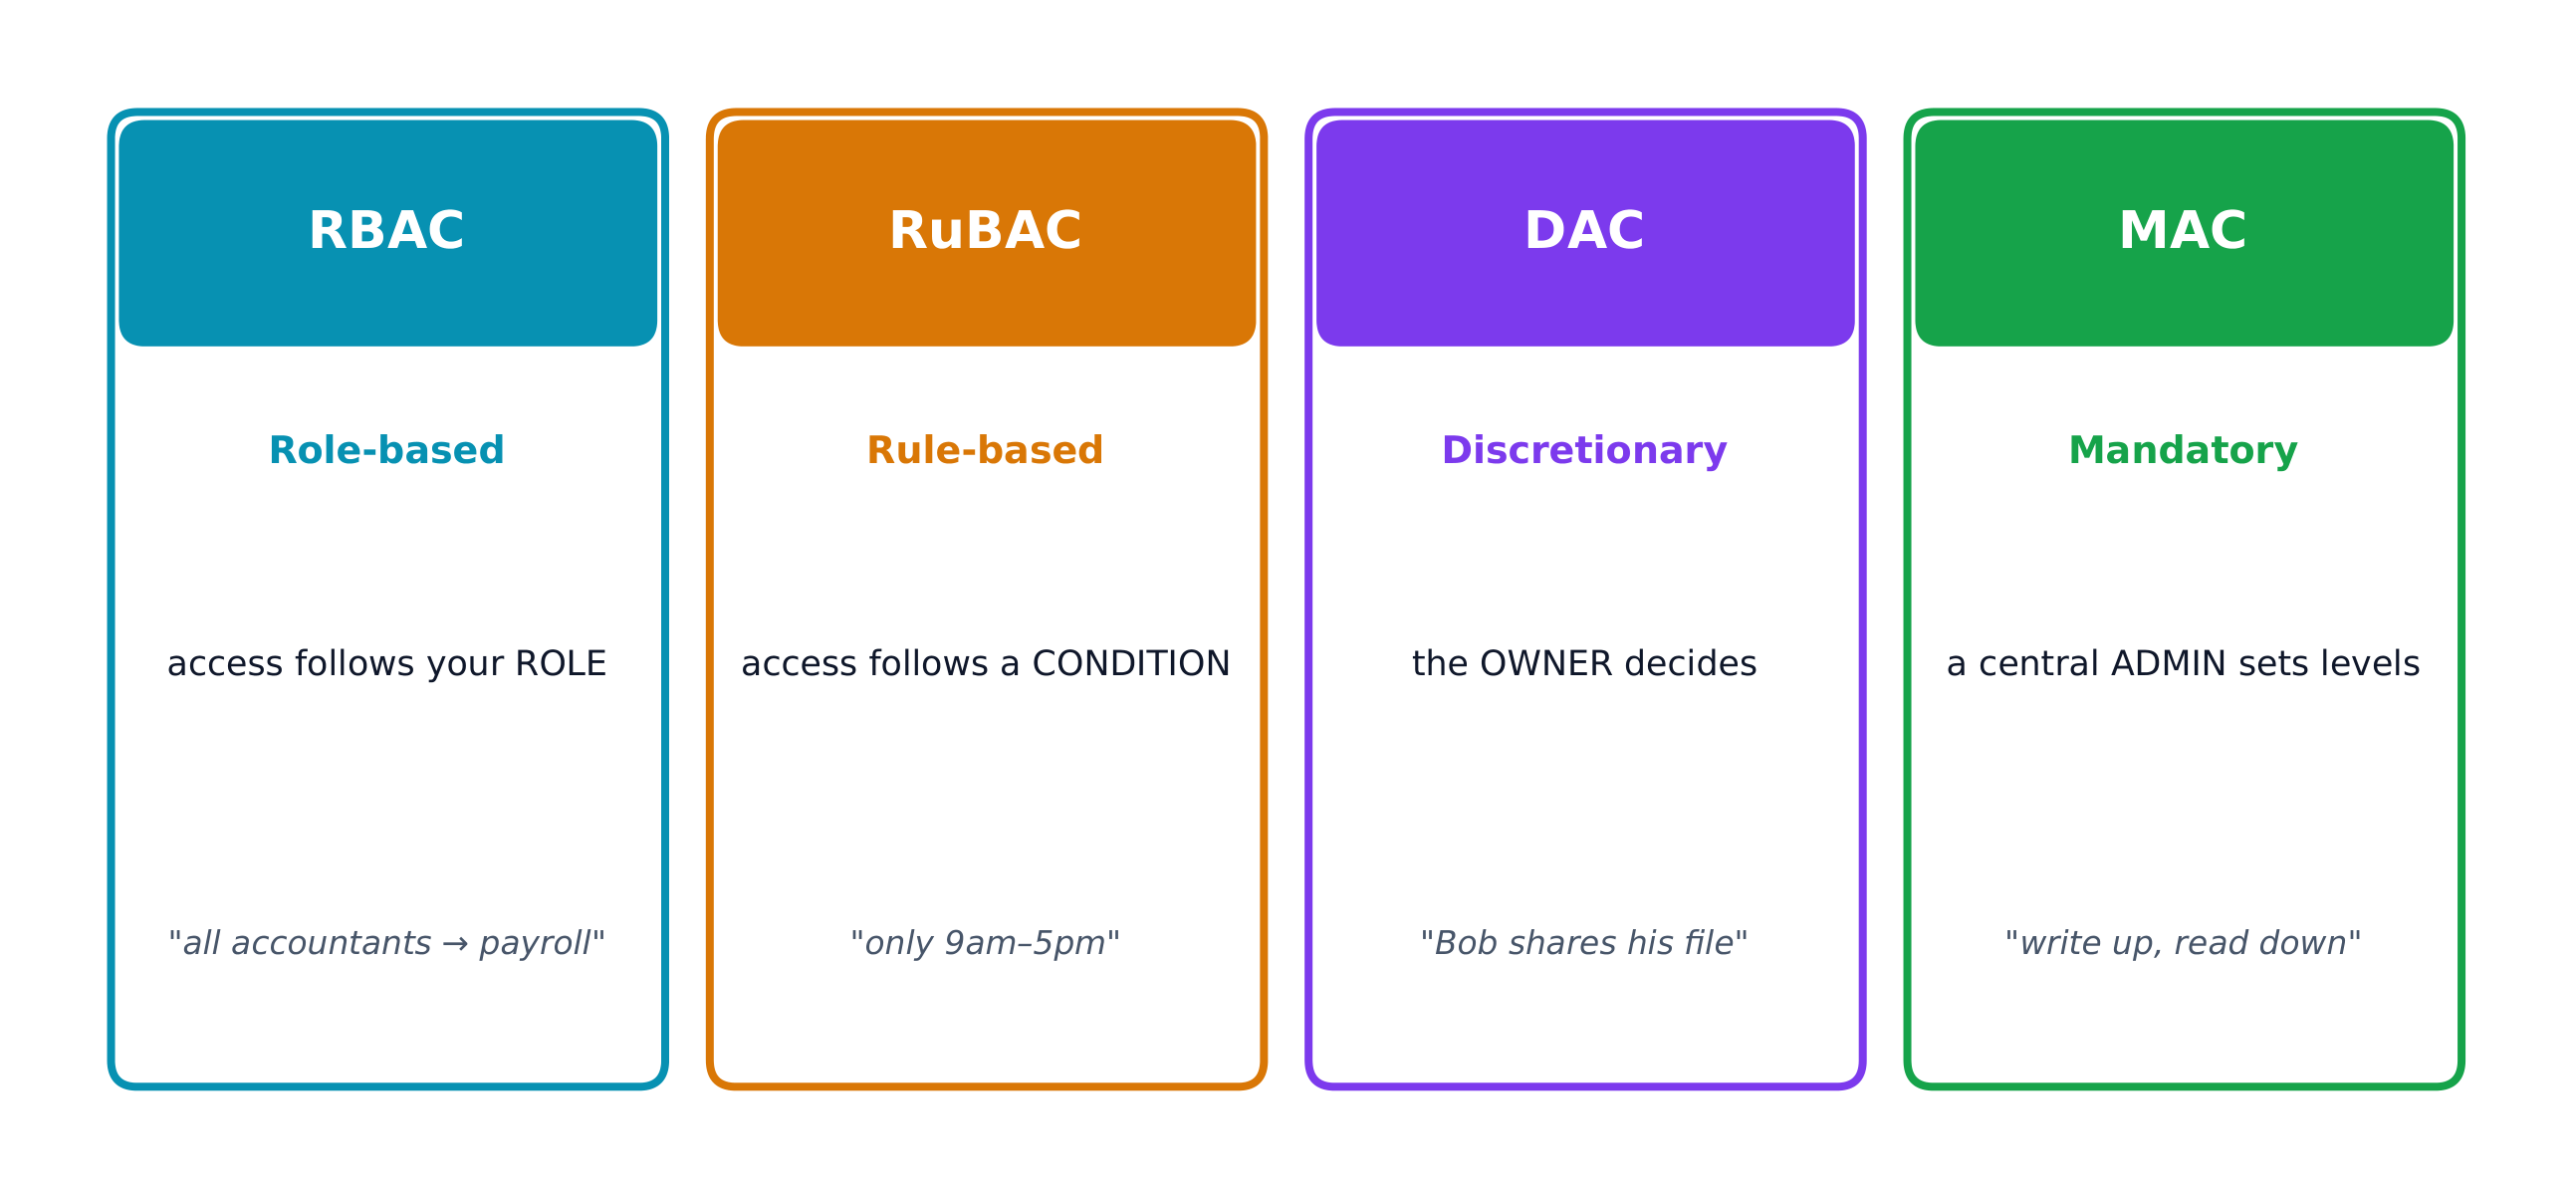
Access control decides which subjects (users) may perform which operations on which objects (files). Four models:
- Role-based (RBAC) 基于角色的访问控制 - access follows your role (all "accountants" reach the payroll software).
- Rule-based (RuBAC) 基于规则的访问控制 - access follows conditions (only during business hours), layered on another model.
- Discretionary (DAC) 自主访问控制 - the owner of a file decides who else may use it.
- Mandatory (MAC) 强制访问控制 - a central administrator sets strict levels; the Bell-LaPadula model summarises it as "write up, read down".
A guiding idea across all models is the principle of least privilege 最小权限原则 - give each entity exactly the access it needs and no more.
On a Linux system, each file has three permissions - read (r), write (w), execute (x) - for three groups: the owner, the group, and others. The chmod command sets them with numbers, adding 4 (read) + 2 (write) + 1 (execute). So chmod 640 means owner read+write (6), group read (4), others nothing (0).
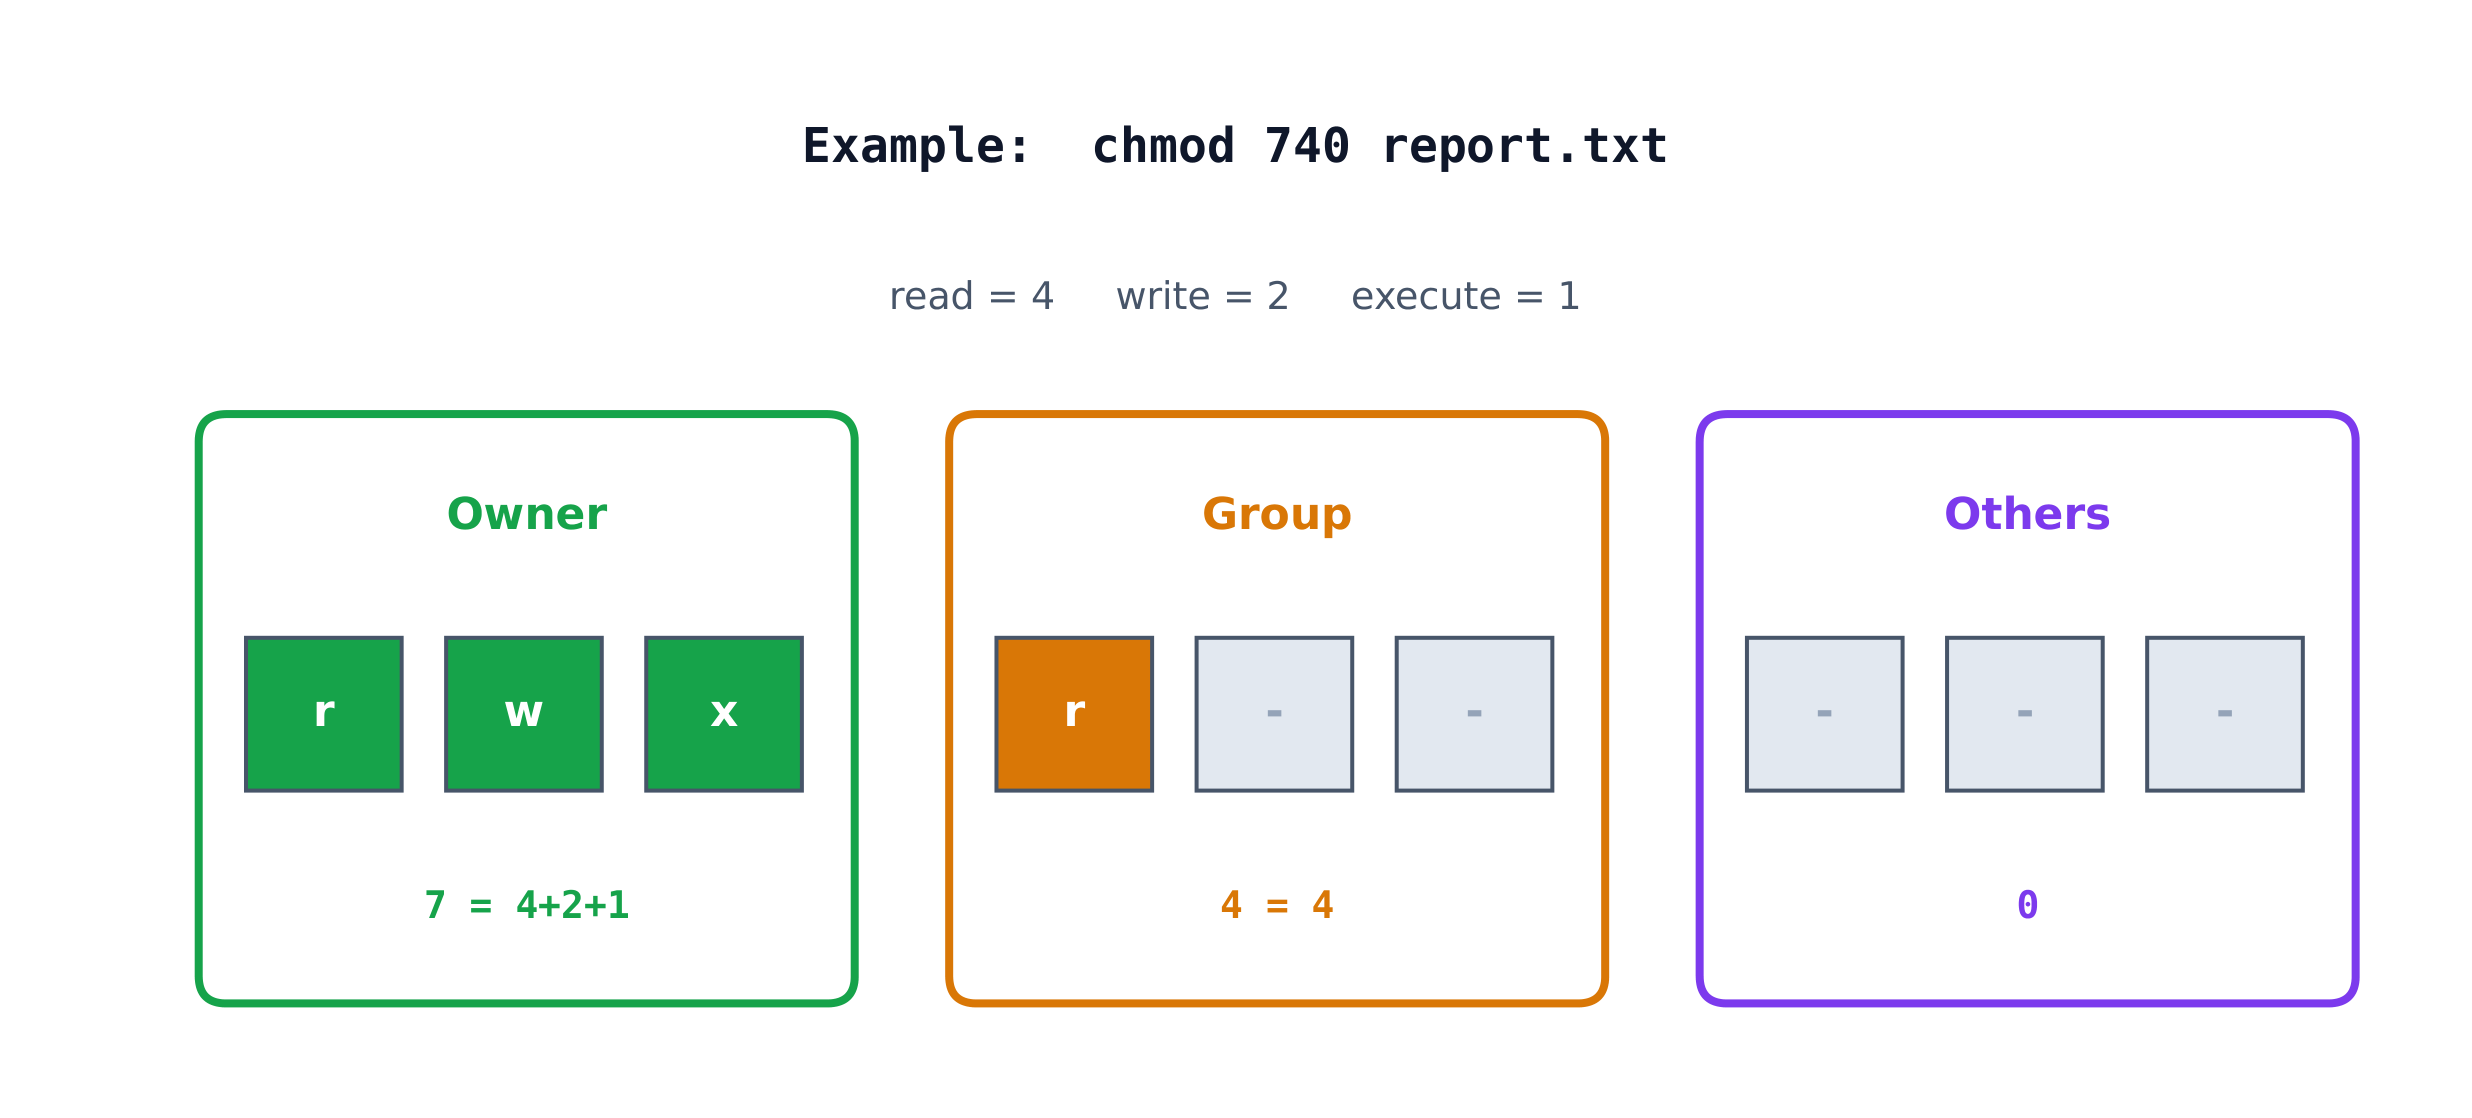
Worked example. A principal wants only herself to read and edit a file, her staff group to read it, and no one else to touch it. Read+write = 4+2 = 6 for the owner, read = 4 for the group, nothing = 0 for others, giving chmod 640 file. The listing then shows -rw-r-----. To also let the owner run the file as a program you would add execute (7 = 4+2+1), giving chmod 740.
Explore
Which access-control model fits the rule?
Each access-control model has a different decider: RBAC by your role, RuBAC by a condition, DAC by the file's owner, and MAC by a central administrator's levels.
Vocabulary
Train
| English |
|---|
| at rest/æt rest/ |
| in transit/ɪn ˈtrænsɪt/ |
| in use/ɪn juːs/ |
| regulated/ˈreɡjʊleɪtɪd/ |
| compliance/kəmˈplaɪəns/ |
| personally identifiable information (PII)/ˈpɜːsənəli aɪˈdentɪfaɪəbl ˌɪnfəˈmeɪʃn/ |
| protected health information (PHI)/prəˈtektɪd helθ ˌɪnfəˈmeɪʃn/ |
| payment card information (PCI)/ˈpeɪmənt kɑːd ˌɪnfəˈmeɪʃn/ |
| Role-based (RBAC)/rəʊl beɪst/ |
| Rule-based (RuBAC)/ruːl beɪst/ |
| Discretionary (DAC)/dɪˈskreʃənəri/ |
| Mandatory (MAC)/ˈmændətəri/ |
| principle of least privilege/ˈprɪnsɪpl ɒv liːst ˈprɪvɪlɪdʒ/ |
5.3
Protecting Stored Data with Cryptography

Syllabus
| Learning Objective | Essential Knowledge |
|---|---|
5.3.A |
|
5.3.B |
|
Source: College Board AP Course and Exam Description
Cryptography 密码学 uses mathematical techniques to protect information and support checks such as authenticity and integrity. An encryption algorithm combines the plaintext 明文 with a key 密钥 to produce ciphertext 密文; decryption reverses it. The keyspace 密钥空间 is the set of possible keys. A fully variable n-bit key has $2^n$ possible values. A larger space can increase exhaustive-search work, but practical security also depends on the algorithm and implementation.
Symmetric encryption 对称加密 uses the same key to encrypt and decrypt. The standard is AES 高级加密标准, a block cipher 分组密码 that works on 128-bit blocks and secures Wi-Fi, browsing, and stored files. Because both sides need the same secret key, sharing that key safely is the challenge.

Explore
Encrypt a message by shifting letters
Encryption combines plaintext with a key to make ciphertext. In this simple cipher the key is the shift amount; only someone who knows the shift can decrypt the message back.
Vocabulary
Train
| English |
|---|
| Cryptography/krɪpˈtɒɡrəfi/ |
| plaintext/ˈpleɪntekst/ |
| key/kiː/ |
| ciphertext/ˈsaɪfətekst/ |
| keyspace/ˈkiːspeɪs/ |
| Symmetric encryption/sɪˈmetrɪk enˈkrɪpʃn/ |
| AES/ˌeɪ iː ˈes/ |
| block cipher/blɒk ˈsaɪfə/ |
5.4
Asymmetric Cryptography
Syllabus
| Learning Objective | Essential Knowledge |
|---|---|
5.4.A |
|
5.4.B |
|
5.4.C |
|
Source: College Board AP Course and Exam Description
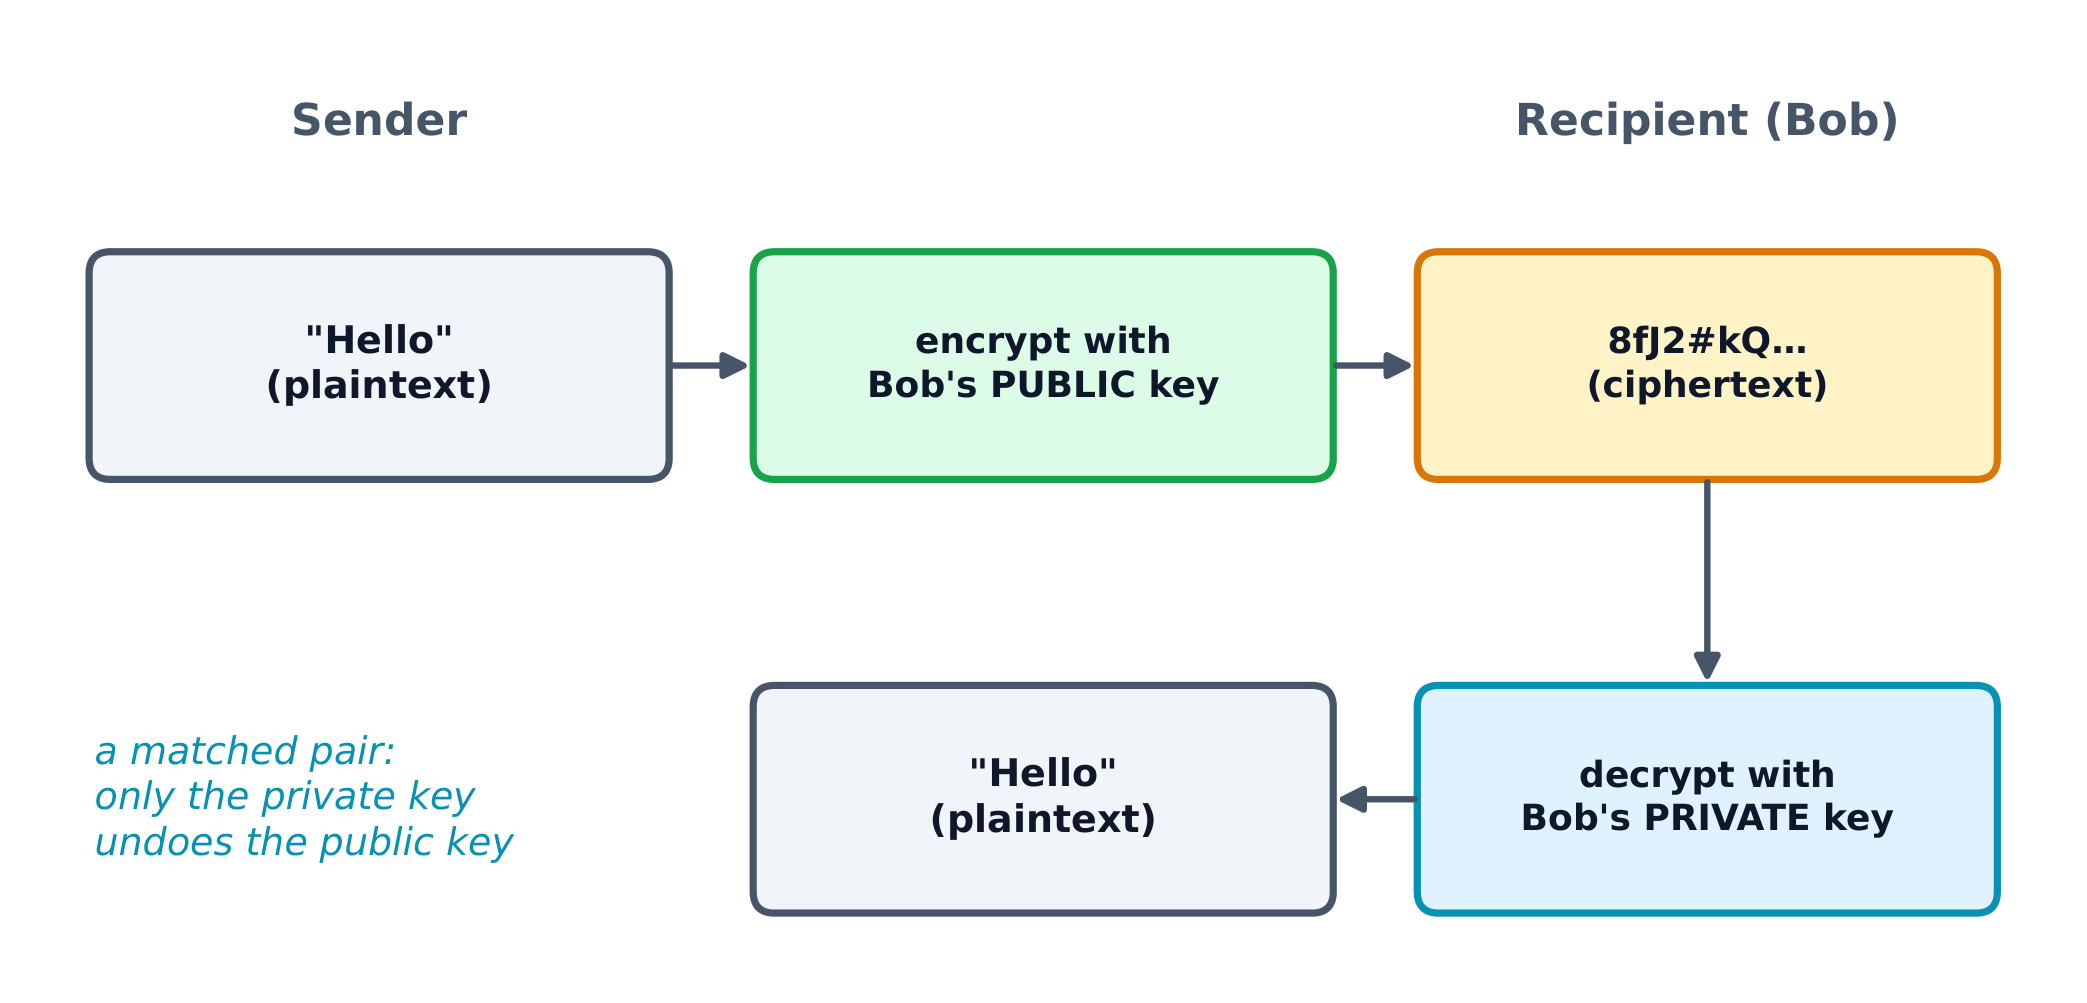
Asymmetric encryption 非对称加密 solves the key-sharing problem with a key pair 密钥对 - a public key 公钥 anyone may see and a private key 私钥 kept secret. Each scheme specifies how its keys are used. For public-key encryption, I encrypt with your public key and you decrypt with your private key. Digital signatures use a private signing key and public verification key; signing is not generally “encrypting with the private key”. The sender must also establish that the public key really belongs to the intended recipient.
Longer keys mean larger keyspaces and more security, but slower encryption. Common asymmetric algorithms are RSA and elliptic curve cryptography (ECC) 椭圆曲线密码学, used in digital signatures and certificates. Remember: you can only compare key lengths within the same algorithm - an RSA 4096-bit key is not directly comparable to an AES 256-bit key.

Vocabulary
Train
| English |
|---|
| Asymmetric encryption/ˌeɪsɪˈmetrɪk enˈkrɪpʃn/ |
| key pair/kiː peə/ |
| public key/ˈpʌblɪk kiː/ |
| private key/ˈpraɪvət kiː/ |
| elliptic curve cryptography (ECC)/ɪˈlɪptɪk kɜːv krɪpˈtɒɡrəfi/ |
5.5
Protecting Applications
Syllabus
| Learning Objective | Essential Knowledge |
|---|---|
5.5.A |
|
5.5.B |
|
Source: College Board AP Course and Exam Description
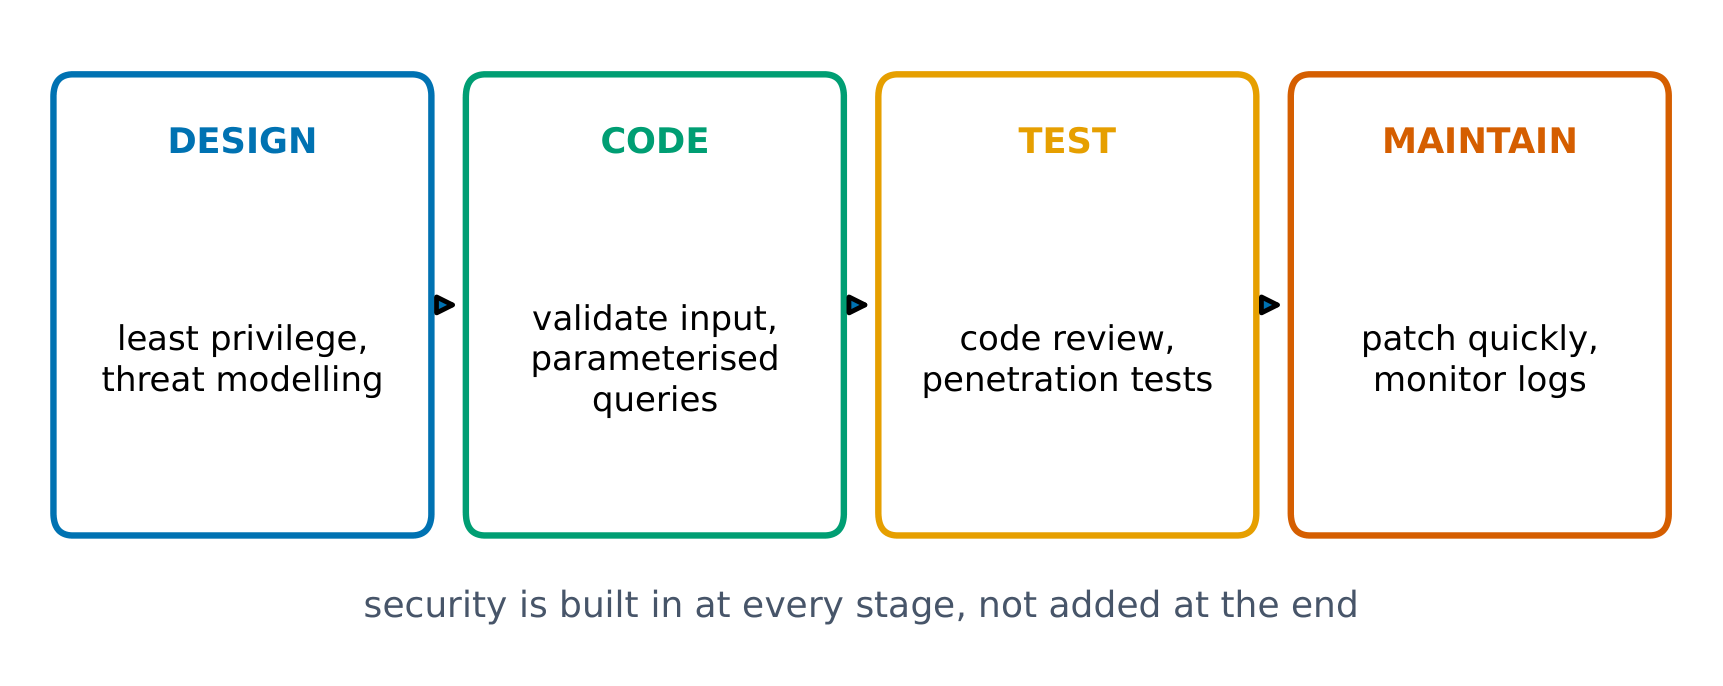
Two design principles keep applications safe from the start. Secure by design 安全设计 builds security into every phase of development, not as an afterthought. Secure by default 默认安全 means the product ships with its security features already enabled - safe straight out of the box.
Secure by design rests on three principles a company must adopt: (1) take ownership of its customers' security outcomes rather than shifting blame onto users, (2) embrace radical transparency and accountability – sharing security-relevant news and updates quickly so everyone becomes safer, and (3) build the organisational structure and leadership that makes security a first-class goal.
Input sanitization 输入清理 transforms input for a specific destination; validation checks an allowed type, length, range or format. Quotes and semicolons are printable special characters 特殊字符, not necessarily control characters. A legitimate name such as O'Neill should remain intact. A single blacklist is not a universal defense: SQL injection needs parameterised queries with separately bound values; XSS needs safe text rendering or output encoding for the destination context (and a suitable HTML sanitizer when HTML is allowed); directory traversal needs resolved paths confined to an allowed directory. For example, 0 OR 1=1 can change an unsafe numeric SQL expression without using quotes or semicolons. Use fixed SQL such as SELECT name FROM pupils WHERE name = ? and bind the entered name separately.
Vocabulary
Train
| English |
|---|
| Secure by design/sɪˈkjʊə baɪ dɪˈzaɪn/ |
| Secure by default/sɪˈkjʊə baɪ dɪˈfɒlt/ |
| input sanitization/ˈɪnpʊt ˌsænɪtaɪˈzeɪʃn/ |
| special characters/ˈspeʃl ˈkærɪktəz/ |
5.6
Detecting Attacks on Data and Applications
Syllabus
| Learning Objective | Essential Knowledge |
|---|---|
5.6.A |
|
5.6.B |
|
5.6.C |
|
5.6.D |
|
5.6.E |
|
Source: College Board AP Course and Exam Description
To detect data attacks, systems perform accounting 审计记录 - logging who accessed what and when. But logs are huge, so log analysis must be automated to run at a useful speed; a human reading raw logs is far too slow. A clever complement is a honeypot 蜜罐 - a fake file that looks valuable; unexpected access gives an alert to investigate. Administrators or scanners may also access a decoy, so an alert alone is not proof of an attack. Watch especially for attempts to delete or copy sensitive files. Cryptographic hashes also help: re-hash a file and compare - if the digest changed, the file was altered.
Choosing detective controls means weighing cost (honeypots are cheap; a data loss prevention (DLP) 数据泄露防护 service is powerful but pricey) against the sensitivity of the data. To read a specific attack from logs, look for its signature: SQL injection shows OR 1=1 and --; XSS shows <script> tags; directory traversal shows ../ sequences; a buffer overflow shows unusually long input strings.
Checking that a file has not been altered
A cryptographic hash turns a file of any size into a short fixed-length value. A change normally gives a different digest, but collisions exist. A match to the publisher's trusted full digest is strong evidence that the bytes match, rather than mathematical proof. You do this at the command line:
| Shell | Command |
|---|---|
| BASH (Linux, and most servers) | sha256sum testfile |
| zsh, the usual terminal on Apple computers | shasum -a 256 testfile |
Both print the SHA-256 hash of testfile. If it differs from the published value by even one character, the file has been altered — by corruption in transit, or by an attacker who replaced it.
⚠️ A hash proves integrity, not authenticity. An attacker who can replace the file on a web page can usually replace the published hash beside it too; that is why a signed hash, or one fetched over a separate trusted channel, is stronger evidence.
Vocabulary
Train
| English |
|---|
| accounting/əˈkaʊntɪŋ/ |
| honeypot/ˈhʌnɪpɒt/ |
| data loss prevention (DLP)/ˈdeɪtə lɒs prɪˈvenʃn/ |
5.6
Exam tips
- Match each application attack to its evidence in a log:
OR 1=1/--= SQL injection;<script>= XSS;../= directory traversal; very long input = buffer overflow. - Learn the four access-control models by their decider: RBAC = your role, RuBAC = a condition, DAC = the file's owner, MAC = a central admin. Least privilege underlies them all.
- Read Linux permissions by adding 4+2+1 per group -
chmod 750= owner rwx (7), group r-x (5), others none (0). Practice converting both ways. - Symmetric = one shared key (fast, AES); asymmetric = a public/private key pair (solves key sharing, RSA/ECC). Encrypt with the recipient's public key.
- Match input defenses to the destination: parameter binding for SQL, context-specific output protection for XSS, and allowed-directory checks for paths. Input sanitization is not one universal character filter; a honeypot is a detective control.
Interactive lessons on this topic
Work through it step by step, with instant-check exercises.