Skip to content · ⁨דלג לתוכן⁩

Introduction to Security · ⁨מבוא לאבטחה⁩

AP Cybersecurity · ⁨אבטחת מידע והסייבר - AP⁩ · Topic 1 · ⁨נושא 1⁩

Video lesson for this topic · ⁨שיעור וידאו לנושא זה⁩ Open the video page · ⁨פתח את עמוד הוידאו⁩
7:55

מבוא לאבטחה

ניתן לבנות קיר מושלם. הצפנה בלתי שבירה, חומות מגן בכל יציאה, טלאים משולבים ביום השחרור. ועדיין, אויב יכול ללכת ישירות…

English narration · English + 中文 subtitles burned in · ⁨קריאת קול באנגלית · תרגום אנגלי + סינית שרוף בתוך הסרטון⁩

1.1

Understanding Social Engineering · ⁨הבנת הנדסה חברתית⁩

Syllabus · ⁨סיילבוס⁩
English

Learning Objective 1.1.A: Identify common indicators of social engineering tactics.

  • 1.1.A.1 Social engineering attacks employ psychological tactics to manipulate users into revealing sensitive information (elicitation), downloading a malicious file, or clicking on a malicious link. Social engineering can be performed in person but is often done by email, by text message, or through social media messages.
  • 1.1.A.2 Adversaries often use psychological tactics like intimidation and urgency to achieve their goals. Intimidation is when an adversary threatens a target with negative consequences if they don’t comply. Urgency is when an adversary creates reasons why a target should act quickly.

Learning Objective 1.1.B: Explain how social engineering tactics influence victims to perform a desired action.

  • 1.1.B.1 Social engineering tactics rely on common psychological principles that influence human behavior.
  • 1.1.B.2 Intimidation leverages a natural human aversion to negative consequences. By drawing attention to possible negative consequences, adversaries use fear to incite targets to act.
  • 1.1.B.3 Urgency leverages a natural human response to react quickly to time-sensitive needs. When targets detect a sense of urgency in a message, they feel pressured to respond or act quickly, which can prevent them from taking the time to consider whether an action is reasonable or safe.

Learning Objective 1.1.C: Describe possible impacts for victims of social engineering attacks.

  • 1.1.C.1 Victims may give an adversary personal information that could lead to impersonation, such as name, phone number, address, workplace, pets’ names, or birthdate. These types of information, and information like them, are often used on websites as challenge questions to verify a user’s identity.
  • 1.1.C.2 Victims may give an adversary secure information like a one-time password (OTP) or authentication login code, which could allow an adversary to log in to a service as the victim.
  • 1.1.C.3 Victims may download malware or click a link that installs malware on their device, steals information from their web browser, or directs them to a website where their login credentials can be captured by an adversary.
עברית

מטרת לימוד 1.1.A: זיהוי סימנים נפוצים של טקטיקות הנדסה חברתית.

  • 1.1.A.1 התקפות הנדסה חברתית משתמשות בטכניקות פסיכולוגיות כדי להניע משתמשים לחשוף מידע רגיש (הוצאת מידע), להוריד קובץ רע או ללחוץ על קישור רע. הנדסה חברתית יכולה להתבצע בפנים אך לרוב נעשית באמצעות דוא"ל, הודעות טקסט או הודעות ברשתות חברתיות.
  • 1.1.A.2 מתקיפים משתמשים לעיתים קרובות בטכניקות פסיכולוגיות כמו הפחד ודחיפות כדי להשיג את מטרתם. הפחד מתרחש כאשר המתקיף מאיים על היעד בתוצאות שליליות אם הוא לא יעשה כפי שנתבקש. דחיפות מתרחשת כאשר המתקיף יוצר סיבות לכך שהיעדaction quickly.

מטרת למידה 1.1.B: הסבר כיצד טקטיקות הנדלן חברתי משפיעות על קורבנות כדי לבצע פעולה רצויה.

  • 1.1.B.1 טקטיקות הנדלן חברתי מתבססות על עקרונות פסיכולוגיים נפוצים המשפיעים על התנהגות אנושית.
  • 1.1.B.2 אינטimidation (הערכה) מנצלת סירוב טבעי של בני אדם לתוצאות שליליות. על ידי משיכת תשומת לב לתוצאות שליליות אפשריות, אויבים משתמשים בחשש כדי לגרם ליעדים לפעול.
  • 1.1.B.3 דחיפות מנצלת תגובה אנושית טבעית להגיב במהירות לצרכים התלויים בזמן. כאשר יעדים מזהים תחושת דחיפות בהודעה, הם מרגישים לחץ להגיב או לפעול במהירות, מה שיכול למנוע מהם לקחת זמן לשקול האם פעולה היא סבירה או בטוחה.

מטרת למידה 1.1.C: תיאור השפעות אפשריות עבור קורבנות של התקפות הנדלן חברתי.

  • 1.1.C.1 הקורבנות עשויים לתת לאויב מידע אישי שיכול להוביל להסתגר, כמו שם, מספר טלפון, כתובת, מקום עבודה, שמות חיות מחמד או תאריך לידה. סוגי מידע אלו, ומידע דומה, משמשים לעיתים קרובות באתרי אינטרנט כשאלות בדיקה כדי לאמת זהות משתמש.
  • 1.1.C.2 הקורבנות עשויים לתת לאויב מידע מאובטח כמו סיסמת חד-פעמית (OTP) או קוד הזדהות, שיכול לאפשר לאויב להתחבר לשירות כקורban.
  • 1.1.C.3 הקורבנות עשויים להוריד תוכנת רוע או ללחוץ על קישור המניח תוכנת רוע על ההתקן שלהם, גנבת מידע מדפדפן האינטרנט שלהם, או הפנייתם לאתר אינטרנט בו את פרטי ההזדהות שלהם יכולים להיות נתפסים על ידי אויב.
Source: College Board AP Course and Exam Description · ⁨מקור: תיאור הקורס והמבחן של College Board AP⁩

English
Phishing: how a fake email steals a password

The weakest part of any computer system is often the human using it. Social engineering 社会工程学 is the art of tricking people into breaking security - giving away a password, opening a bad file, or clicking a bad link. The attacker (we call them an adversary 对手) does not need to break the code; they only need to fool a person.

Most social engineering happens by email, text message, or social media, though it can also happen in person or by phone. The goal is elicitation 套取信息 - getting sensitive information out of someone without them realising.

Adversaries lean on two powerful feelings:

  • Intimidation 恐吓 - the adversary threatens a bad result if you do not obey. Fear pushes you to act.
  • Urgency 紧迫感 - the adversary invents a deadline ("reply in the next hour or your account closes"). When we feel rushed, we stop thinking carefully about whether an action is safe.

The impact 影响 on a victim can be serious. They might reveal personal details (name, address, pet's name, birthday) that are later used to answer security challenge questions 安全问题 and impersonate 冒充 them. They might hand over a one-time password (OTP) 一次性密码, letting the adversary log in as them. Or they might download malware 恶意软件 that steals data from their browser.

Worked example. A phishing email reads: "Over 90% of staff have already verified their account - confirm yours in the next hour or lose payroll access." Two tactics are stacked here. "In the next hour" is urgency (a deadline that rushes you), and "over 90% of staff have already" is consensus (social pressure to follow the crowd). Naming each tactic - not just calling the email "suspicious" - is exactly what an exam answer needs.

עברית
הפישינג: כיצד הודעת דוא"ל מזויפת גנבת סיסמה

החלק החלש ביותר בכל מערכת מחשב הוא לעיתים קרובות האדם האנושי המשמש אותה. הנדסה חברתית היא אמנות ההטיה של אנשים לפעולה המפרה אבטחה - מסירת סיסמה, פתיחת קובץ רע, או לחיצה על קישור רע. התוקף (אנו מכנים אותו אויב) אינו צריך לפרוץ את הקוד; הוא צריך רק לבלבל אדם.

רוב ההנדסה החברתית מתרחשת באמצעות דוא"ל, הודעת טקסט או מדיה חברתית, אך היא עשויה להתרחש גם פנים מול פנים או בטלפון. המטרה היא הוצאת מידע - קבלת מידע רגיש מאדם ללא הבנתו.

תוקפים מסתמכים על שני רגשות חזקים:

  • הרתעה - התוקף מאיים בתוצאה רעה אם לא תתמסר. פחד דוחף אותך לפעולה.
  • דחיפות - התוקף ממציא deadline ("השב תוך שעה או החשבון שלך ייסגר"). כאשר אנו מרגישים בלחץ, מפסיקים לחשוב בזהירות על בטיחות פעולה.
הנדסה חברתית משתמשת בלחץ פסיכולוגי כדי להניע קורבן לפעולה לפני שהוא חושב
הנדסה חברתית משתמשת בלחץ פסיכולוגי כדי לגרום לקורבן לפעול לפני שהוא חושב

ההשפעה על קורבן עשויה להיות חמורה. הוא עשוי לחשוף פרטים אישיים (שם, כתובת, שם חיית מחמד, תאריך לידה) שייועדו בהמשך לתשובות על שאלות בטיחות ולהתחלפות זהות. הוא עשוי למסור סיסמת פעם אחת (OTP), המאפשרת לאויב להתחבר כמותו. או שהוא עשוי להוריד תוכנת זיהום הגונבת נתונים מהדפדפן שלו.

דוגמה מפורטת. מייל פישिंग נוסח כך: "יותר מ-90% מהעובדים כבר אימתו את החשבון שלהם - אימתו את שלכם בשעה הקרובה או אבדתם גישה לשכר." כאן משולבים שני טקטיקות. "בשעה הקרובה" היא דחיפות (מועד סיום דוחק), ו"יותר מ-90% מהעובדים כבר" היא הסכמה (לחץ חברתי לעקוב אחר המון). ציין כל טקטיקה – ולא רק לכנות את המייל "חשוד" – זה בדיוק מה שנדרש בתשובת מבחן.

Explore · ⁨חקור⁩

Which social-engineering tactic is it? · ⁨איזה טקטיקה הנדסה חברתית זו?⁩

Intimidation threatens harm, urgency invents a deadline, consensus claims everyone else is doing it, and authority pretends to have power over you. · ⁨הרתעה מאיימת על נזק, דחיפות ממציאה אחרון, הסכמה טוענת שכולם האחרים עושים זאת, וסמכות מתגייסת לכוח מעליו.⁩

Vocabulary · ⁨מילון מונחים⁩ Train · ⁨אימון⁩
English עברית
Social engineering/ˈsəʊʃl ˌendʒɪˈnɪərɪŋ/ הנדסה חברתית
adversary/ˈædvəsəri/ יריב
elicitation/ɪˌlɪsɪˈteɪʃn/ הוצאת מידע
Intimidation/ɪnˌtɪmɪˈdeɪʃn/ הרתעה
Urgency/ˈɜːdʒənsi/ דחיפות
impact/ˈɪmpækt/ השפעה
challenge questions/ˈtʃælɪndʒ ˈkwestʃnz/ שאלות אתגר
impersonate/ɪmˈpɜːsəneɪt/ התחלפות זהות
one-time password (OTP)/wʌn taɪm ˈpæswɜːd/ סיסמת פעם אחת (OTP)
malware/ˈmælweə/ תוכנה רעה
password attack/ˈpæswɜːd əˈtæk/ תקפת סיסמה
weak/wiːk/ חלשה
dictionary/ˈdɪkʃənəri/ מילון
authentication/ɔːˌθentɪˈkeɪʃn/ אימות
password manager/ˈpæswɜːd ˈmænɪdʒə/ מנהל סיסמות
multifactor authentication (MFA)/ˌmʌltɪˈfæktə ɔːˌθentɪˈkeɪʃn/ אישור רב-שלבתי (MFA)
exploits/ˈeksplɔɪts/ ניצול חוסר אבטחה
phishing/ˈfɪʃɪŋ/ דייפישינג
shared secret/ʃeəd ˈsiːkrɪt/ סוד משותף
AI-enhanced coding tools/ˌeɪ ˈaɪ enˈhænst ˈkəʊdɪŋ tuːlz/ כלי תכנות מחוזקים באמצעות בינה מלאכותית
vulnerabilities/ˌvʌlnərəˈbɪlɪtiz/ נקודות חולשה
threat detection and response/θret dɪˈtekʃn ænd rɪˈspɒns/ זיהוי איומים ותגובה אליהם
1.2

Suspicious Website Logins · ⁨התחברויות לאתרים חשודים⁩

Syllabus · ⁨סיילבוס⁩
English

Learning Objective 1.2.A: Identify common signs of a password attack.

  • 1.2.A.1 In an online password attack, adversaries try logging in to a device or service using common passwords, common password patterns, or stolen passwords.
  • 1.2.A.2 Signs of an online password attack include:
    • Many failed attempts to log in over a short duration
    • Login attempts at unusual times
    • Login attempts from unknown devices

Learning Objective 1.2.B: Explain how adversaries take advantage of weak authentication.

  • 1.2.B.1 Many people use common patterns when creating passwords, such as:
    • Starting a password with one or two words, adding a two-digit number (often signifying a year), and putting a special character at the end
    • Including the names of family or pets in their passwords
    • Including personally significant dates in their passwords
  • 1.2.B.2 Adversaries often construct a dictionary of possible passwords based on personal information gathered about a target (e.g., birthday, anniversary, names of pets and family) and use an automated tool to submit potential passwords.

Learning Objective 1.2.C: Explain how to make authentication stronger.

  • 1.2.C.1 Users should create passwords that are long, random, and unique. A password manager can be used to generate and store strong passwords, or a user may create long, unique passphrases for their accounts.
  • 1.2.C.2 When creating passwords, users should avoid names, dates, or other personally meaningful words or numbers.
  • 1.2.C.3 When available, users should enable multifactor authentication (MFA), which will require the user to provide extra proof of identity—such as a one-time code—in addition to the password as an extra layer of security.
עברית

מטרת למידה 1.2.A: זיהוי סימנים נפוצים של התקפת סיסמה.

  • 1.2.A.1 בהתקפת סיסמה אונליין, אויבים מנסים להתחבר להתקן או לשירות באמצעות סיסמות נפוצות, דפוסי סיסמה נפוצים או סיסמות גנובות.
  • 1.2.A.2 סימנים להתקפת סיסמה אונליין כוללים:
    • מספר רב של ניסיונות התחברות כושלים בתוך תקופת זמן קצרה
    • ניסיונות התחברות בשעות בלתי שגרתיות
    • ניסיונות התחברות ממכשירים לא מוכרים

מטרת למידה 1.2.B: הסבר כיצד אויבים מנצלים אימות חלש.

  • 1.2.B.1 אנשים רבים משתמשים בדפוסי סיסמה נפוצים בעת יצירת סיסמות, כמו:
    • התחלת סיסמה במילה אחת או שתי מילים, הוספת מספר דו-ספרתי (לרוב המייצג שנה), והכנסת character מיוחד בסוף
    • כללת שמות של בני משפחה או חיות מחמד בסיסמות שלהם
    • כללת תאריכים בעלי משמעות אישית בסיסמות שלהם
  • 1.2.B.2 תוקפים לעיתים קרובות בונים מילון של סיסמאות אפשריות על בסיס מידע אישי שנאסף על אודות יעד (למשל, יום הולדת, יום שנה, שמות חיות מחמד ומשפחה) ומשתמשים בכלי אוטומטי כדי להגיש סיסמאות פוטנציאליות.

מטרת למידה 1.2.C: הסבר כיצד לחזק את האישור.

  • 1.2.C.1 משתמשים צריכים ליצור סיסמאות ארוכות, אקראיות וייחודיות. ניתן להשתמש במנהל סיסמאות כדי ליצור ולשמור סיסמאות חזקות, או שמשתמש עשוי ליצור ביטויי מעבר ארוכים וייחודיים לחשבונותיו.
  • 1.2.C.2 בעת יצירת סיסמאות, משתמשים צריכים להימנע משמות, תאריכים או מילים ומספרים אחרים בעלי משמעות אישית.
  • 1.2.C.3 כאשר זה זמין, משתמשים צריכים להפעיל אישור רב-שלבי (MFA), שידרוש מהמשתמש לספק הוכחת זהות נוספת—כגון קוד חד-פעמי—בנוסף לסיסמה כשכבת ביטחון נוספת.

Source: College Board AP Course and Exam Description · ⁨מקור: תיאור הקורס והמבחן של College Board AP⁩

English

A password attack 密码攻击 is any attempt to log in using guessed or stolen passwords. In an online password attack the adversary tries passwords against a real login page. The warning signs are visible in the logs:

  • many failed logins in a short time,
  • login attempts at unusual hours,
  • login attempts from unknown devices.

Adversaries succeed because people choose weak 弱 passwords. Common patterns include a word plus a two-digit year plus a special character (like Summer24!), or a pet's or family member's name. Because these patterns are so common, an adversary can build a dictionary 字典 of likely passwords from information gathered about you and let an automated tool try each one.

To make authentication 身份验证 stronger:

  • Create passwords that are long, random, and unique - a password manager 密码管理器 can generate and store them for you.
  • Avoid names, dates, and meaningful words.
  • Turn on multifactor authentication (MFA) 多因素身份验证, which asks for extra proof (like a texted code) on top of the password.
עברית
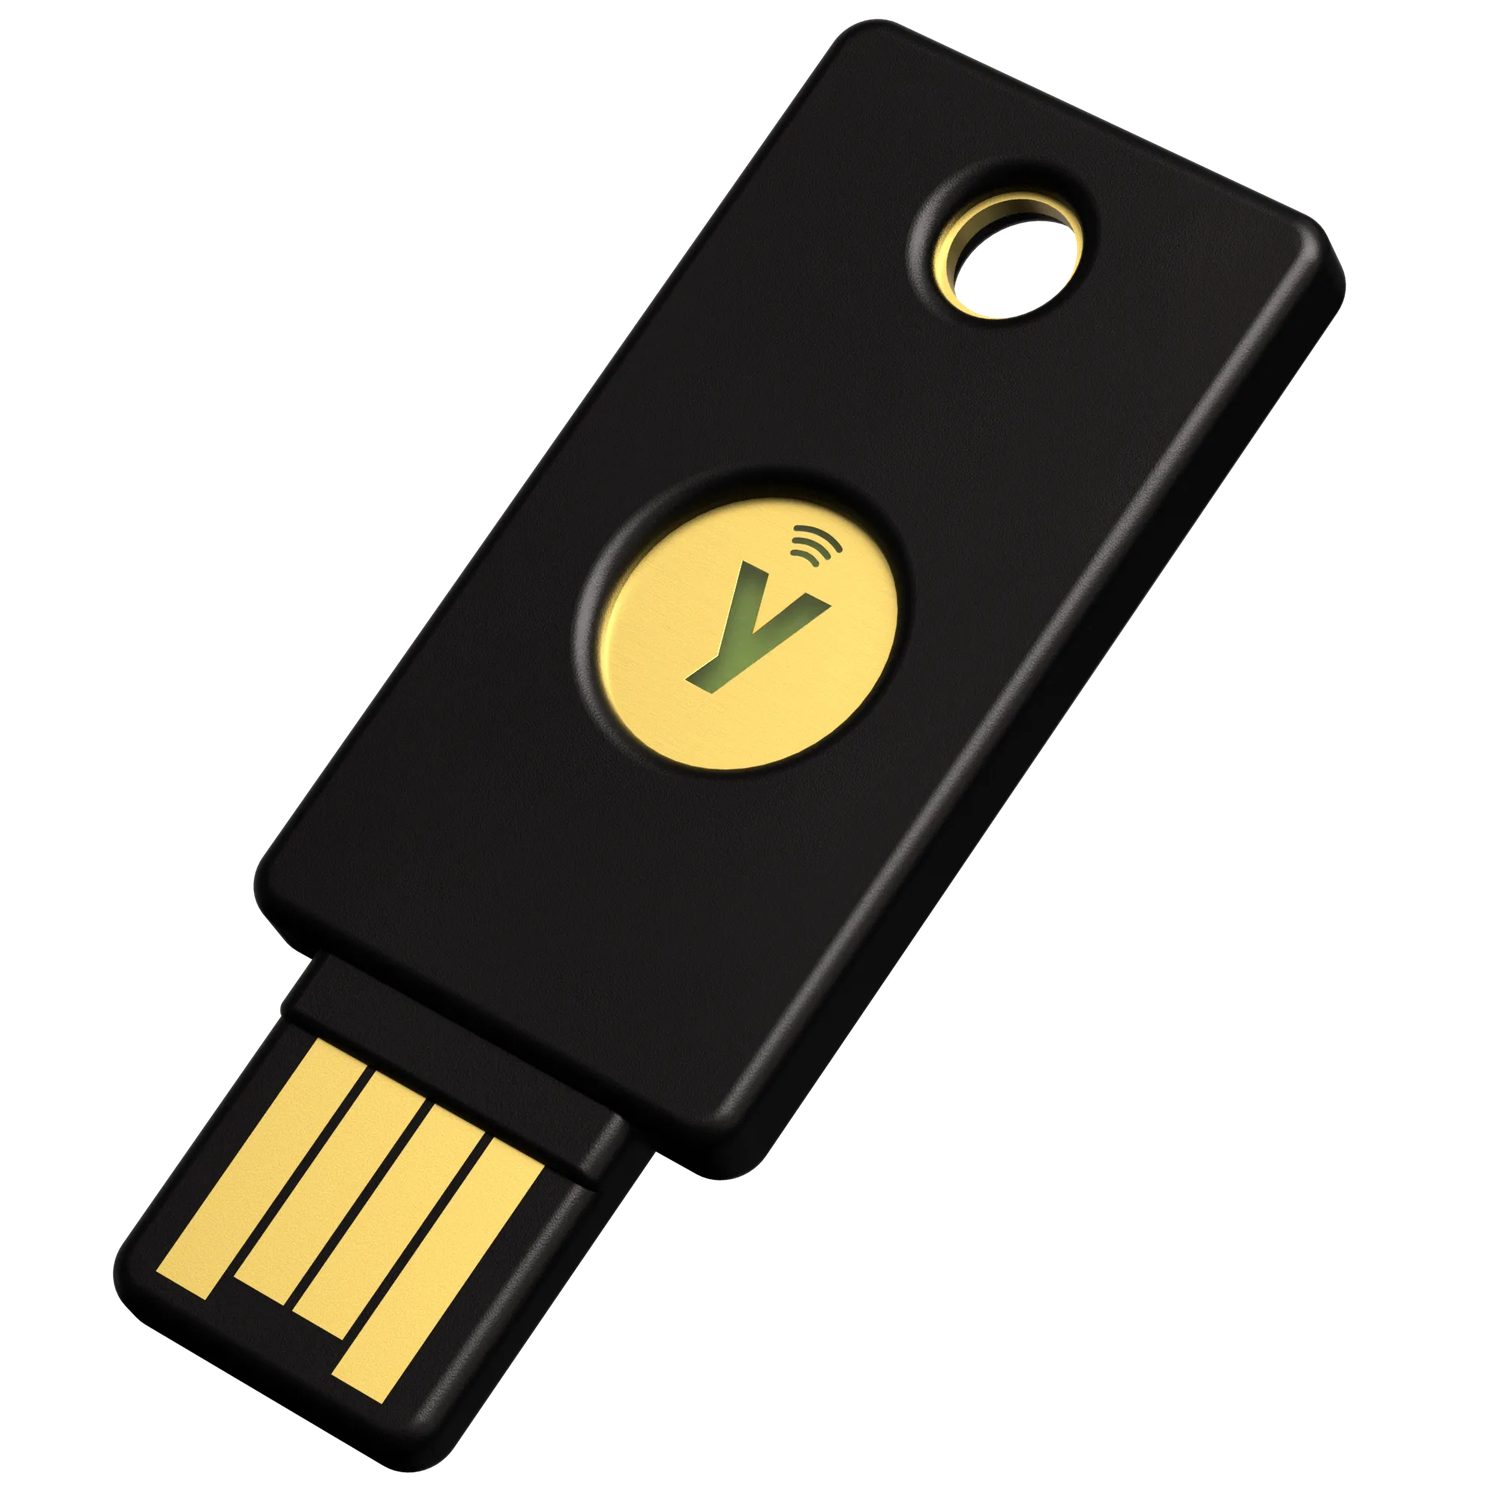
מפתח ביטוח חומרה: אימות חזק מפחית נזקים כאשר סיסמה מופקשת בפישिंग

התקפת סיסמה היא כל ניסיון התחברות באמצעות סיסמות שמחושבות או גנובות. בהתקפת סיסמה אונליין האויב מנסה סיסמות מול דף התחברות אמיתי. סימני ההתראה נראים ביומני ההתחברות:

  • מספר רב של התחברויות נכשלות בטווח זמן קצר,
  • ניסיונות התחברות בשעות לא שגרתיות,
  • ניסיונות התחברות ממכשירים לא מוכרים.

לאויבים מצליח מכיוון שהאנשים בוחרים סיסמות חלשות. דפוסים נפוצים כוללים מילה בתוספת שנה בעלת שתי ספרות ותווית מיוחדת (כמו Summer24!), או שם של חיית מחמד או של בן משפחה. מכיוון שדפוסים אלו נפוצים מאוד, לאויב יכול לבנות מילון של סיסמות סבירות מתוך מידע שנאסף עליו ולהפעיל כלי אוטומטי שיעלה כל אחד מהם.

כדי להפוך את האימות לחזק יותר:

  • צור סיסמות ארוכות, אקראיות וייחודיות – מנהל סיסמות יכול ליצור אותן ולשמור אותן עבורך.
  • הימנע משמות, תאריכים ומילים בעלות משמעות.
  • הפעל אימות רב-גורמי (MFA), הדורש הוכחה נוספת (כמו קוד שנשלח בטקסט) מעבר לסיסמה.
1.3

Best Practices for Public Networks · ⁨שיטות עבודה מיטביות ברשתות ציבוריות⁩

Syllabus · ⁨סיילבוס⁩
English

Learning Objective 1.3.A: Identify the type of adversary conducting a cyberattack.

  • 1.3.A.1 Adversaries can be classified by their skill levels.
    • Low-skilled adversaries rely on malicious cyber tools created by others that can be purchased online. The tools they use exploit known vulnerabilities.
    • High-skilled adversaries have the capacity to create new malicious cyber tools or modify existing ones to adapt to new defensive techniques and tools. They also have the capacity to discover undocumented vulnerabilities, known as zero days.
  • 1.3.A.2 Adversaries have a variety of motivations, including greed, desire for recognition, dedication to a cause, revenge, politics, or beliefs.

Learning Objective 1.3.B: Identify types of wireless cyberattacks.

  • 1.3.B.1 In an evil twin attack, an adversary sets up their own wireless access point (WAP) with a service set identifier (SSID) similar or identical to a target network; the adversary’s network is called the evil twin. Victims of this attack could select to unknowingly connect to the evil twin, allowing the adversary to capture their network traffic. The adversary cannot read traffic that uses an encrypted protocol like HTTPS.
  • 1.3.B.2 In a jamming attack, an adversary floods an area with a strong electromagnetic (EM) signal in the same frequency range as the wireless network, which prevents legitimate traffic between the access point (AP) and users. This type of attack that prevents users from accessing resources is called a denial of service (DoS) attack.
  • 1.3.B.3 In a war driving attack, adversaries try to detect wireless network beacons while driving or walking around a target. If a wireless signal is detected, the adversary can gather information about the type of wireless network used and find areas where the wireless signal extends outside the physical building.

Learning Objective 1.3.C: Describe actions individuals can take to increase protection of sensitive data when using the internet and Wi-Fi.

  • 1.3.C.1 Individuals should verify that the name of any wireless network they join exactly matches the name of the network they intend to join.
  • 1.3.C.2 Most internet protocols are encrypted to protect network traffic. However, individuals may consider the sensitivity of their data in choosing whether to join unencrypted Wi-Fi networks to protect vulnerable data such as DNS queries.
  • 1.3.C.3 Individuals may consider using a virtual private network (VPN), which encrypts all their traffic to the VPN operator’s system. Although this action prevents a service provider from viewing traffic, the VPN provider can view the traffic.
עברית

מטרת למידה 1.3.A: זיהוי סוג התוקף המבצע התקפה سایبرנית.

  • 1.3.A.1 תוקפים יכולים להיות מסווגים לפי רמות המיומנות שלהם.
    • תוקפים בעלי מיומנות נמוכה מתבססים על כלים سایberניים רעים שנוצרו על ידי אחרים ועלולים לקנות באינטרנט. הכלים שהם משתמשים בהם מנצלים תקלות ידועות.
    • תוקפים בעלי מיומנות גבוהה יש להם את היכולת ליצור כלים سایberניים רעים חדשים או לשנות קיימים כדי להתאים לשיטות וכלי הגנה חדשים. הם גם יש להם את היכולת לגלות תקלות שאינן מסודרות, הנקראות 'ימים אפס' (zero days).
  • 1.3.A.2 לתוקפים יש מגוון של מניעים, כולל תאבה, רצון להכרה, מחויבות למטרה, נקמה, פוליטיקה או אמונות.

מטרת למידה 1.3.B: זיהוי סוגי התקפות سایberניות אלחוטיות.

  • 1.3.B.1 בהתקפת 'אחיות רעה' (evil twin), תוקף מקים נקודת גישה אלחוטית (WAP) משלו עם מזהה סט שירות (SSID) דומה או זהה לרשת יעד; הרשת של התוקף נקראת אחיות רעה. קורבנות ההתקפה עשויים לבחור, מבלי לדעת, להתחבר לאחיות הרעה, מה שמאפשר לתוקף לצלם את תנועת הרשת שלו. התוקף אינו יכול לקרוא תנועה המשמשת פרוטוקול מאופיין כמו HTTPS.
  • 1.3.B.2 בהתקפת הפרעה (jamming), תוקף מטביע אזור בסמן אלקטרומגנטי (EM) חזק בטווח התדרים אותו טווח של הרשת האלחוטית, מה שמונע תנועה חוקית בין נקודת הגישה (AP) למשתמשים. סוג התקפה זו המונעת ממשתמשים לגשת למשאבים נקראת התקפת סירוב שירות (DoS).
  • 1.3.B.3 בהתקפת נהיגת מלחמה (war driving), תוקפים מנסים לזהות אותות גישה של רשתות אלחוטיות בזמן נהיגה או הליכה סביב יעד. אם נזהה אות אלחוט, התוקף יכול לאסוף מידע על סוג הרשת האלחוטית המשמשת ולמצוא אזורים בהם האות האלחוט משתרע מחוץ למבנה הפיזי.

מטרת למידה 1.3.C: תיאור פעולות שיכולים לנקוט פרטים כדי להגדיל את ההגנה על נתונים רגישים בעת השימוש באינטרנט וב-Wi-Fi.

  • 1.3.C.1 פרטים צריכים לוודא ששם כל רשת אלחוטית אליה הם מצטרפים תואם בדיוק לשם הרשת שכוונתם להצטרף אליה.
  • 1.3.C.2 רוב פרוטוקולי האינטרנט מאופיינים כדי להגן על תנועת הרשת. עם זאת, פרטים עשויים לשקול את רגישות הנתונים שלהם בבחירה אם להצטרף לרשתות Wi-Fi לא מאופיינות כדי להגן על נתונים רגישים כגון בקשות DNS.
  • 1.3.C.3 פרטים עשויים לשקול להשתמש ברשת פרטית וירטואלית (VPN), שמאפייה את כל תנועתם למערכת ספק ה-VPN. למרות שהפעולה הזו מונעת מספק שירות לצפות בתנועה, ספק ה-VPN יכול לצפות בתנועה.

Source: College Board AP Course and Exam Description · ⁨מקור: תיאור הקורס והמבחן של College Board AP⁩

English

Not all adversaries are the same. We classify them by skill: low-skilled attackers buy ready-made tools online and reuse known exploits 漏洞利用, while high-skilled attackers write their own tools and can discover brand-new holes called zero days 零日漏洞. Their motivation 动机 varies too - greed, revenge, politics, or belief.

Public Wi-Fi is a favourite hunting ground. Three wireless attacks you must know:

  • Evil twin 双胞胎恶意热点 - the adversary sets up a fake access point 接入点 with a name (SSID 服务集标识符) copied from the real network. Victims connect to the fake one, and the adversary reads their traffic (though encrypted 加密的 sites like HTTPS stay safe).
  • Jamming 干扰攻击 - the adversary floods the air with a strong radio signal so no one can connect. This is one kind of denial of service (DoS) 拒绝服务 attack.
  • War driving 战争驾驶 - the adversary drives around detecting wireless networks and where their signal leaks outside a building.

To protect yourself on public networks: check that the network name exactly matches the one you intend to join, prefer encrypted sites, and consider a virtual private network (VPN) 虚拟专用网络, which encrypts all of your traffic to the VPN operator.

עברית
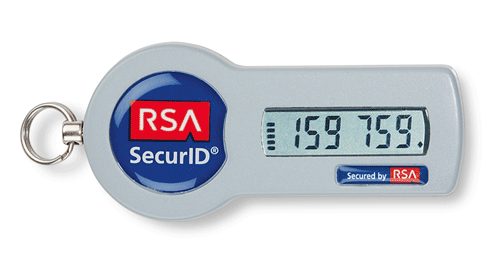
סימן ביטחון: קודים חד-פעמיים וסימנים מונעים התחברות המסתמכת רק על סיסמה
token ביטוח: קודים וטוקנים לפעם אחת מונעים שהתחברות בסיסמה בלבד תהיה מספקת

לא כל האויבים זהים. אנו מסווגים אותם לפי מיומנות: תקפי מיומנות נמוכה קונים כלים מוכנים באינטרנט ומשתמשים ב-ניצולים ידועים שוב ושוב, בעוד תקפי מיומנות גבוהה כותבים את הכלים שלהם ויכולים לגלות חורים חדשים לחלוטין הנקראים Zero Days. ה-מוטיבציה שלהם גם כן משתנה – תאובה, נקמה, פוליטיקה, או אמונה.

Wi-Fi ציבורי הוא מקום צידה מועדף. שלוש התקנות אלחוטיות שאתה חייב לדעת:

  • אח תמים רשע – האויב מציג נקודת גישה מזויפת עם שם (SSID) העתק מהרשת האמיתית. הקורבנות מתחברים לזה הזויף, והאויב קורא את התנועה שלהם (אם כי אתרי מוצפנים כמו HTTPS נשארים בטוחים).
  • הפרעה (Jamming) – האויב ממלא את האוויר עם אות רדיו חזק כך שאף אחד לא יכול להתחבר. זוהי אחת מסוגי ההתקנות של פגיעה בשירות (DoS).
  • War driving - השודד נהג סביב כדי לזהות רשתות אלחוטיות ולאתר היכן אותן הן דולפות מחוץ למבנה.
נקודת גישה של שד כפול מעתיקה את שם הרשת האמיתית כך שהקורבנות יתחברו לשודד

כדי להגן על עצמך ברשתות ציבוריות: ודא שהשם מתאים בדיוק לרשת שאתה מתכוון להתחבר אליה, העדף אתרים מוצפנים, והתחשב בשימוש ב-רשת פרטית וירטואלית (VPN), המצפירה את כל התנועה שלך לצד מפעיל ה-VPN.

Vocabulary · ⁨מילון מונחים⁩ Train · ⁨אימון⁩
English עברית
zero days/ˈzɪərəʊ deɪz/ אפס ימים
motivation/ˌməʊtɪˈveɪʃn/ הנעה
Evil twin/ˈiːvl twɪn/ אח הארוך הרשע
access point/ˈækses pɔɪnt/ נקודת גישה
SSID/ˌes es aɪ ˈdiː/ SSID
encrypted/enˈkrɪptɪd/ מוצפן
Jamming/ˈdʒæmɪŋ/ הפרעה מכוונת (Jamming)
denial of service (DoS)/dɪˈnaɪəl ɒv ˈsɜːvɪs/ מניעת שירות (DoS)
War driving/wɔː ˈdraɪvɪŋ/ נהיגת מלחמה (War driving)
virtual private network (VPN)/ˈvɜːtʃuːəl ˈpraɪvət ˈnetwɜːk/ רשת פרטית וירטואלית (VPN)
1.4

AI-Based Cybersecurity Attacks · ⁨התקפות אבטחה ממוחשבת מבוססות בינה מלאכותית⁩

Syllabus · ⁨סיילבוס⁩
English

Learning Objective 1.4.A: Explain how adversaries use AI-powered tools to augment cyberattacks.

  • 1.4.A.1 Adversaries can use AI-powered tools that leverage existing voice and image samples of a person to create a digital avatar of that person. The use of these technologies enables adversaries to impersonate someone over the phone or even on a video call, which can lead to financial loss or the sharing of sensitive or private information. As more organizations adopt voice-based authentication, the impact of voice-impersonation has a larger potential impact.
  • 1.4.A.2 Adversaries can use generative AI tools, like large language models (LLMs), to create convincing phishing messages in any target language. Because traditional phishing messages are sometimes written by non-native speakers of the target’s language, unnatural language is a feature that has been used to distinguish phishing messages from legitimate messages. However, with AI tools, adversaries can now craft phishing messages in any language that read as though they were written by a native speaker.
  • 1.4.A.3 Adversaries can craft prompts that extract secure or sensitive information from LLMs. Secure or sensitive information in LLMs can come from user input and the large data sets used to train LLMs.
  • 1.4.A.4 Adversaries can publish websites or modify existing websites to contain false information so that the false information will be included in the training sets for LLMs, causing the LLMs to repeat the false information.
  • 1.4.A.5 Adversaries can perform reconnaissance on a target using AI-powered tools that scan the internet to gather information posted on social media and public websites.
  • 1.4.A.6 Adversaries can use AI-enhanced coding tools to help them write new malware, modify existing application code to perform malicious activities, or to find vulnerabilities in large code bases.

Learning Objective 1.4.B: Explain how to protect against some AI-augmented cyberattacks.

  • 1.4.B.1 Shared secrets with close friends and relatives that can be used to verify each other’s identities should be established. A secret word or phrase known only to two parties can be used to authenticate identities in high-stakes situations.
  • 1.4.B.2 Multifactor authentication (MFA) should be enabled. If an adversary clones a target’s voice to access a system with voice authentication, requiring a second authentication factor could prevent an adversary from gaining access to accounts.
  • 1.4.B.3 Personal or sensitive data should not be entered into any AI-powered tools, such as chatbots or virtual assistants. Some AI-powered tools feed user input back into the model to provide continuous training. Adversaries could extract data that users have included in prompts.
  • 1.4.B.4 Output from AI-powered tools should be carefully evaluated. Verify information from AI-powered tools using reputable, stable, non-AI-based sources.
עברית

מטרות למידה 1.4.A: הסבר כיצד מתקיפים משתמשים בכלי תומכי בינה מלאכותית כדי להגביר את ההתקפות הקיברנטיות.

  • 1.4.A.1 מתקיפים יכולים להשתמש בכלי תומכי בינה מלאכותית המנצלים דוגמאות קול וציור קיימות של אדם כלשהו ליצירת תמונת גוף דיגיטלית (avatar) שלו. שימוש בטכנולוגיות אלו מאפשר לתוקף להתחלף באופן טלפוני או אפילו בשיחת וידאו, מה שעלול לגרום לנזקים כספיים או לחשיפת מידע רגיש או פרטי. ככל שהארגונים רבים מאמצים אימות מבוסס קול, כך הפוטנציאל לאפקט הרסני של החלפה בקול גדל.
  • 1.4.A.2 מתקיפים יכולים להשתמש בכלי בינה מלאכותית יוצרת, כמו מודלי שפה גדולים (LLMs), ליצירת הודעות פישिंग מרשעות בכל שפת יעד. מכיוון שהודעות פישिंग מסורתיות נכתבות לעיתים על ידי דוברי שפה שאינם דוברי אם-שפה של היעד, לשון לא טבעית היא מאפיין ששימש להבחנה בין הודעות פישिंग לבין הודעות חוקיות. עם זאת, עם כלי AI, מתקיפים יכולים כעת לכתוב הודעות פישिंग בכל שפה שנשמעות כאילו נכתבו על ידי דובר אם-שפה.
  • 1.4.A.3 מתקיפים יכולים לכתוב פרומפטים שמצליחים לחלץ מידע מאובטח או רגיש ממודלי שפה גדולים (LLMs). מידע מאובטח או רגיש ב-LLMs יכול להגיע מקלט המשתמש ומסטיות הנתונים הגדולות ששימשו לאימון המודלים.
  • 1.4.A.4 מתקיפים יכולים לפרסם אתרי אינטרנט או לשנות אתרי אינטרנט קיימים כדי שיכללו מידע שקרי, כך שהמידע השקר יכלל בסטיות האימון של ה-LLMs, מה שגורם להם לחזור ולשנות את המידע השקר.
  • 1.4.A.5 מתקיפים יכולים לבצע סקירה על היעד באמצעות כלי תומכי בינה מלאכותית לסריקת האינטרנט לצורך איסוף מידע שפורסם ברשתות חברתיות ובאתרים ציבוריים.
  • 1.4.A.6 מתקיפים יכולים להשתמש בכלי כתיבת קוד מוגברים על ידי AI כדי לעזור להם לכתוב תוכנת זיהוי חדשה, לשנות קוד אפליקציה קיים כדי לבצע פעולות מזיקות, או למצוא נקודות תורפה במאגרי קוד גדולים.

מטרות למידה 1.4.B: הסבר כיצד להגן על עצמם מפני חלק מההתקפות הקיברנטיות התומכות בבינה מלאכותית.

  • 1.4.B.1 יש לקבוע סודות משותפים עם חברים קרובים ומשפחה שניתן להשתמש בהם לאימות זהות הדדי. מילה או משפט סודי המוכר רק לשתי הצדדים יכול לשמש לאימות זהות במקרים בעלי סיכון גבוה.
  • 1.4.B.2 יש להפעיל אימות רב-גורמי (MFA). אם מתקיף שחיק את קולו של היעד כדי לגשת למערכת עם אימות קולי, דרישה לגורם אימות נוסף עשויה למנוע ממנו לגשת לחשבונות.
  • 1.4.B.3 נתונים אישיים או רגישים לא צריכים להיות מוזנים לכלי תומכי בינה מלאכותית, כמו בוטים או עוזרים וירטואליים. חלק מהכלים הללו מעבירים את קלט המשתמש חזרה לדגם כדי לספק אימון רציף. מתקיפים יכולים לחלץ נתונים שהמשתמשים כללו בפרומפטים.
  • 1.4.B.4 יש לבצע בדיקה קפדנית של התוצאות מכלי תומכי בינה מלאכותית. יש לוודא מידע מכלי תומכי בינה מלאכותית באמצעות מקורות אמין, יציב ולא מבוסס AI.

Source: College Board AP Course and Exam Description · ⁨מקור: תיאור הקורס והמבחן של College Board AP⁩

English

Artificial intelligence gives adversaries powerful new tools. With enough voice and image samples, an adversary can build a deepfake 深度伪造 avatar to impersonate someone on a call. Large language models (LLMs) 大语言模型 let them write convincing phishing 钓鱼 emails in perfect, native-sounding language - removing the clumsy wording that once gave scams away.

AI also helps adversaries on the back end: crafting prompts that pull secret data out of an LLM, planting false information on websites so it poisons an LLM's training data, scanning the internet to gather facts about a target, and even writing new malware.

You can defend against many AI-augmented attacks: agree on a shared secret 共享秘密 word with close contacts to verify identity, enable MFA (so a cloned voice alone cannot log in), never type sensitive data into a chatbot, and always double-check AI output against reliable, non-AI sources.

AI writes code, and that cuts both ways. Adversaries use AI-enhanced coding tools 人工智能辅助编程工具 to write new malware faster than they could by hand, to modify existing application code so that it performs malicious activity, and to scan a codebase for vulnerabilities 漏洞 to attack. The skill barrier falls: someone who could not previously write an exploit can now ask for one, so the number of capable attackers rises even when no new technique is invented.

עברית

בינה מלאכותית מספקת לשודדים כלים חדשים וחזקים. עם מספיק דגימות קול ותמונה, יכול השודד לבנות תמונת פנים מזויפת (deepfake) כדי להסתיר תחת זהותו של מישהו שיחה. מודלי שפה גדולים (LLMs) מאפשרים להם לכתוב אימיילי פישינג משכנעים בשפה טבעית ומקומית מושלמת - ובכך לבטל את הניסוח המבוכה שמיהר בעבר לחשוף את ההונאה.

בינה מלאכותית עוזרת גם לשודדים בחלק האחורי: יצירת פרומפטים שמייצאים נתונים סודיים ממודל שפה גדול, השתלת מידע שקרי באתרים כדי לפגוע בנתוני האימון של המודל, סריקת האינטרנט לאיסוף מידע על מטרה, ואף כתיבת תוכנת זדון חדשה.

ניתן להגן על עצמך מרבים מההתקפות המוגברות באמצעות בינה מלאכותית: הסכם על מילה סודית משותפת עם אנשים קרובים כדי לאמת זהות, הפעל אימות רב-שלבי (כך שרק קול משתלה לא יהיה מספיק להתחבר), לעולם אל תכניס נתונים רגישים לתוך בוט צ'אט, ובכל פעם בדוק את תוצרי הבינה המלאכותית מול מקורות אמין שאינו מבוסס בינה מלאכותית.

בינה מלאכותית כותבת קוד, ויש לכך שני צדדים. השודדים משתמשים בכלי כתיבת קוד מוגברים באמצעות בינה מלאכותית כדי ליצור תוכנת זדון חדשה מהר יותר מאשר יכלו לעשות ידנית, לשנות קוד אפליקציות קיים כדי שיבצע פעילות מזדה, ולסרוק בסיס קוד חיפוש נקודות חולשה להתקפה. מחסום הכישרון יורד: מי שלא ידע לפני כן לכתוב ניצול יכול כעת לבקש אותו, ולכן מספר המתקיפים המיומנים עולה גם כאשר לא נמצא טכניקה חדשה.

Vocabulary · ⁨מילון מונחים⁩ Train · ⁨אימון⁩
English עברית
deepfake/ˈdiːpfeɪk/ דיפפקייק
Large language models (LLMs)/lɑːdʒ ˈlæŋɡwɪdʒ ˈmɒdlz/ מודלי שפה גדולים (LLMs)
1.5

Leveraging AI in Cyber Defense · ⁨ניצול בינה מלאכותית בהגנה سایبرית⁩

Syllabus · ⁨סיילבוס⁩
English

Learning Objective 1.5.A: Explain how cyber defenders can leverage AI-powered tools to protect networks, applications, and data.

  • 1.5.A.1 AI tools can review current security configurations, like firewall rules and access controls, and recommend more secure options. Recommendations should always be checked by a knowledgeable security technician before being implemented.
  • 1.5.A.2 AI-powered tools can analyze application code to identify vulnerabilities and recommend mitigations. Recommendations should always be reviewed by a knowledgeable programmer before being implemented.
  • 1.5.A.3 AI-powered tools can suggest rules for automated detection systems. Detection rules should always be reviewed by a knowledgeable detection engineer before being added to a system.

Learning Objective 1.5.B: Explain how AI-powered tools are enabling faster and more accurate threat detection and response.

  • 1.5.B.1 Of the millions of digital events that happen on networks daily, some likely represent an adversary conducting malicious activity. Humans cannot carefully examine all those events to identify the malicious activity.
  • 1.5.B.2 AI-powered tools can be trained to quickly analyze digital events and sort the events that are likely malicious activity from those that are harmless.
  • 1.5.B.3 AI-powered tools can be programmed to alert human cybersecurity personnel when likely malicious activity is detected or to take specific corrective actions based on the type of malicious activity detected.
  • 1.5.B.4 AI-powered tools enable threat-detection and response teams to catch malicious activity and intervene quickly to prevent loss, harm, damage, and destruction to digital infrastructure and data.
עברית

מטרות למידה 1.5.A: הסבר כיצד מגינים קיברנטיים יכולים לנצל כלי תומכי בינה מלאכותית כדי להגן על רשתות, אפליקציות ומידע.

  • 1.5.A.1 כלבי AI יכולים לבדוק תצורות אבטרה נוכחיות, כמו כללי חומות אש ושליטת גישה, ולהמליץ על אפשרויות מאובטחות יותר. המלצות אלו צריכות תמיד להיות נבדקות על ידי טכנאי אבטחה מיומן לפני ביצוען.
  • 1.5.A.2 כלבי AI יכולים לנתח קוד אפליקציה כדי לזהות נקודות תורפה ולהמליץ על מניעה. המלצות אלו צריכות תמיד להיות נבדקות על ידי מתכנת מיומן לפני ביצוען.
  • 1.5.A.3 כלבי AI יכולים להציע כללים למערכות זיהוי אוטומטיות. כללי זיהוי אלו צריכים תמיד להיות נבדקים על ידי מהנדס זיהוי מיומן לפני הוספתם למערכת.

מטרות למידה 1.5.B: הסבר כיצד כלי תומכי בינה מלאכותית מאפשרים זיהוי ותגובה לאיומים מהירים ומדויקים יותר.

  • 1.5.B.1 מבין מיליוני האירועים הדיגיטליים שקורים ברשתות מדי יום, חלקם ככל הנראה מייצגים פעילות מזיקה של מתקיף. אנשים אינם יכולים לבדוק בקפדנות את כל האירועים הללו כדי לזהות את הפעילות המזיקה.
  • 1.5.B.2 כלבי AI יכולים להיות מאומנים כדי לנתח במהירות אירועים דיגיטליים ולמיון את האירועים שעלולים להיות פעילות מזיקה מאלו שהם חסרי סיכון.
  • 1.5.B.3 כלים המופעלים על ידי בינה מלאכותית יכולים להיכנס לתוכנית כדי לזהיר אישיות אבטחת מידע אנושית כאשר מתגלה פעילות רעה סבירה, או לבצע פעולות תיקון ספציפיות בהתבסס על סוג הפעילות הרעה שזוהתה.
  • 1.5.B.4 כלים המופעלים על ידי בינה מלאכותית מאפשרים לצוותי זיהוי איומים ותגובה לתפוס פעילות רעה ולתערב במהירות למניעת נזק, פגיעה, הרס וה destruction (השמדה) לתשתית דיגיטלית ולמידע.

Source: College Board AP Course and Exam Description · ⁨מקור: תיאור הקורס והמבחן של College Board AP⁩

English

The same technology defends us. AI tools can analyse an application's own source code, identify vulnerabilities in it and recommend mitigations; they can also review firewall rules and access settings and recommend safer options - though a human expert must always check the advice before applying it. AI can scan application code for weaknesses and suggest detection rules.

⚠️ A recommendation is not a fix. The CED is explicit that the advice must be reviewed and implemented by a knowledgeable programmer: an AI tool can be confidently wrong about whether a flaw is exploitable, and applying a suggested patch without understanding it can introduce a new fault of its own.

Its biggest advantage is scale. A medium network produces millions of events every day - far too many for people to read. AI can quickly sort the harmless events from the likely-malicious ones, alert human staff, or take an automatic action. This lets defenders catch an attack and respond in seconds instead of days, preventing loss and damage.

That scale is what makes threat detection and response 威胁检测与响应 possible in practice: an AI system flags malicious activity as it happens, so the response team can intervene quickly enough to prevent loss, harm, or destruction of digital infrastructure — rather than reading the logs days later and finding out what was taken.

עברית

אותה טכנולוגיה מגנה עלינו. כלי בינה מלאכותית יכולים לנתח קוד מקור של אפליקציה, לזהות נקודות חולשה בהן ולהציע פתרונות להפחתת הסיכון; הם יכולים גם לסדר כללי אשכולות וקביעות גישה ולהציע אופציות בטוחות יותר - אם כי יש לוודא תמיד כי מומחה אנושי בדק את ההמלצה לפני יישוםה. בינה מלאכותית יכולה לסרוק קוד אפליקציה לחיפוש חולשות ולהציע כללי זיהוי.

⚠️ המלצה אינה תיקון. ה-CED מדגיש במפורש שההמלצה חייבת להיות נבדקת ומומשת על ידי מתכנת מומחה: כלי בינה מלאכותית יכול להיות בטוח לגמרי שגוי לגבי יכולת ניצול פגם, ויישום תיקון מוצע ללא הבנתו יכול להכניס תקלה חדשה משלו.

היתרון הגדול ביותר שלו הוא הקנה מידה. רשת בגודל בינוני מייצרת מיליוני אירועים ביום - הרבה מדי עבור אנושים לקרוא. בינה מלאכותית יכולה למיין במהירות אירועים חסרי סיכון מאירועים שנראים כמזדונים, להציג התראה לצוות האנושי, או לנקוט בפעולה אוטומטית. הדבר מאפשר להגנה לזהות התקפה ולהגיב בתוך שניות ולא ימים, ולמנוע נזק ואובדן.

הקנה מידה הזה הוא מה ש_make_ זיהוי איומים והגיבה אפשרי בפועל: מערכת בינה מלאכותית מסמנת פעילות מזדה בזמן אמת, כך צוות ההגיבה יכול להתערב במהירות מספיק כדי למנוע אובדן, נזק או הרס תשתית דיגיטלית - במקום לקרוא את הלוגים ימים לאחר מכן ולגלות מה נלקח.

1.5

Exam tips · ⁨טיפים לבחינות⁩

English
  • When a question asks you to rank risks, remember high risk = high impact AND easy to exploit. A parking-lot Wi-Fi leak matters less than an open internal port that lets an adversary spoof a device.
  • Learn the social-engineering tactics by name - intimidation, urgency, pretexting, authority, consensus, scarcity, familiarity - and be ready to spot which one an email is using.
  • Encryption still protects you on an evil twin: the adversary sees your traffic but cannot read HTTPS. Say what is exposed, not just "it's unsafe".
  • For "how to make authentication stronger", MFA is almost always part of the answer, plus long/unique passwords from a manager.
  • AI is dual-use: the same tool (LLMs, code analysis) appears on both the attack and the defense side. Read the question carefully to see which side it asks about.
עברית
  • כאשר שאלה מבקשת ממך למיין סיכונים, זכור ש-סיכון גבוה = השפעה גבוהה AND קל לניצול. דליפת Wi-Fi בחניה פחותה משמעותית מאשר פורט פנימי פתוח המאפשר לשודד להסתיר תחת זהות התקן.
  • למד את טקטיקות ההנדסה החברתית בשמם - הארגה, דחיפות, הקמה, סמכות, קונסנס, מחסור, מכריות - והתכונן לזהות איזה אחד מהן משתמש אימייל נתון.
  • הצפנה עדיין מגנה עליך מול שד כפול: השודד רואה את התנועה שלך אך לא יכול לקרוא HTTPS. אמור מה נחשף, ולא רק "זה לא בטוח".
  • עבור "איך לחזק אימות", MFA היא כמעט תמיד חלק מהתשובה, בנוסף למילים קרות/יחודיות מנהל מילים קוד.
  • בינה מלאכותית היא שימוש כפול: אותו כלי (LLMs, ניתוח קוד) מופיע גם בצד ההתקפה וגם בצד ההגנה. קרא את השאלה בקפדנות כדי לראות באיזה צד היא שואלת.

Interactive lessons on this topic · ⁨שיעורים אינטראקטיביים בנושא זה⁩

Work through it step by step, with instant-check exercises. · ⁨לעבור על הדברים צעד אחר צעד, עם תרגילים לבדיקה מיידית.⁩

Past Papers · ⁨מבחני עבר⁩

More topics in AP Cybersecurity · ⁨אבטחת מידע והסייבר - AP⁩ · ⁨נושאים נוספים בAP Cybersecurity · ⁨אבטחת מידע והסייבר - AP⁩⁩

Log in or create account · ⁨היכנס או צור חשבון⁩

IGCSE, A-Level & AP