Symmetric encryption · 对称加密
This page needs a recent browser (with SharedArrayBuffer support). Please update Chrome, Edge, Firefox or Safari to the latest version. · 此页面需较新浏览器(支持 SharedArrayBuffer)。请升级 Chrome、Edge、Firefox 或 Safari 至最新版本。
English
Locking with a key
- Encryption scrambles a message so only someone with the key can read it.
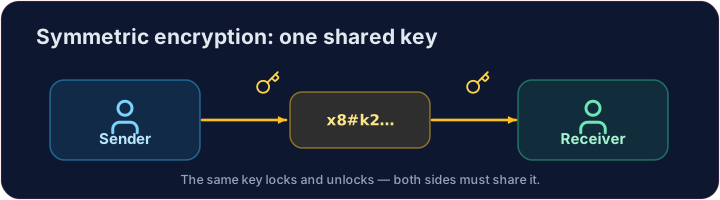
- In symmetric encryption, the same key locks and unlocks. Sender and receiver must both know it.
中文
用密钥上锁
- 加密把消息打乱,使得只有持有密钥的人才能读懂。
- 在对称加密中,同一把密钥既上锁也解锁。发送方和接收方都必须知道它。
English
The Caesar cipher
- The oldest example: shift every letter forward by a fixed number. With shift 3,
a → d,b → e, and so on. - The key is the shift. Decrypting just shifts back.
中文
凯撒密码
- 最古老的例子:把每个字母向后移动固定的位数。移动 3 位时,
a → d、b → e,以此类推。 - 密钥就是这个位移量。解密只需反向移动。
text = "attack"
shift = 3
out = "".join(chr((ord(c) - 97 + shift) % 26 + 97) for c in text)
print(out)        # dwwdfn
English
Why Caesar is weak
- There are only 25 possible shifts, so a computer can try them all in a blink.
- This is a brute-force attack on the key — exactly what real encryption must resist.
中文
凯撒密码为什么弱
- 一共只有 25 种可能的位移,所以计算机一眨眼就能全部试完。
- 这就是对密钥的暴力破解攻击 —— 而真正的加密必须能抵抗它。
English
What real ciphers do
- Modern symmetric ciphers like AES use keys with billions of billions of possibilities.
- The big problem they leave: how do two people share the secret key safely? The next lesson solves it.
Covers: IGCSE 2.3 (symmetric encryption), A-Level 17.1.
中文
真正的密码做了什么
- 像 AES 这样的现代对称密码,密钥拥有亿亿种可能。
- 它们留下的大难题是:两个人如何安全地共享这把密钥? 下一课来解决它。
涵盖:IGCSE 2.3(对称加密)、A-Level 17.1。
English
Common mistakes
- One shared key both encrypts and decrypts.
- The hard part is sharing that key safely.
中文
常见错误
- 一把共享密钥既加密又解密。
- 难点在于安全地共享这把密钥。
Explore · 探索
Symmetric encryption · 对称加密
The Caesar cipher uses one shared key to encrypt and decrypt. · 凯撒密码用一个共享密钥来加密和解密。
Encrypt hello with a Caesar cipher · 凯撒密码: shift each letter forward by shift places (wrapping past z back to a). Build the encrypted string and print it. · 用凯撒密码加密 hello:把每个字母向后移 shift 位(超过 z 就绕回 a)。构造出加密后的字符串并打印它。
Click Run to see the output here. · 点击“运行”查看此处输出。
Now break it — that is why Caesar is weak. You intercepted cipher, and you suspect the plaintext is attack. Try every shift from 1 to 25, shifting back · 反向, and print the shift that turns cipher into · 生成 attack. · 现在来破解它 —— 这正是凯撒密码弱的原因。你截获了 cipher,并且怀疑明文是 attack。把每个 1 到 25 的位移都试一遍(往回移),打印能把 cipher 变成 attack 的那个位移。
Click Run to see the output here. · 点击“运行”查看此处输出。