Passwords and authentication · 비밀번호 및 인증
This page needs a recent browser (with SharedArrayBuffer support). Please update Chrome, Edge, Firefox or Safari to the latest version. · 이 페이지는 최신 브라우저(SharedArrayBuffer 지원)가 필요합니다. Chrome, Edge, Firefox 또는 Safari를 최신 버전으로 업데이트해 주세요.
English
Proving who you are
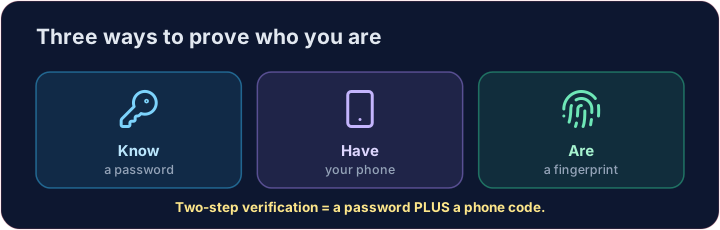
- Authentication means proving you are who you claim to be. There are three classic ways:
- Something you know (a password), something you have (a phone), something you are (a fingerprint).
한국어
본인의 신원 증명하기
- 인증(Authentication) 은 본인이声称한的那个人身份。有三个经典的方法:
- 당신이 아는 것(비밀번호), 당신이 가지고 있는 것(휴대폰), 당신이 본인임 (지문).
English
Stronger logins
- Biometrics — fingerprints or face scans; hard to steal, but not perfect.
- Two-step verification (2FA) — a password plus a one-time code sent to your phone.
- Even if an attacker steals your password, 2FA stops them logging in.
한국어
더 강력한 로그인
- 생체 인증 — 지문이나 얼굴 스캔; 도난하기 어렵지만 완벽하지는 않다.
- 2단계 인증 (2FA) — 비밀번호 에 추가하여 휴대폰으로 전송된 일회용 코드 사용.
- 공격자가 비밀번호를 훔치더라도 2FA가 로그인을 차단한다.
English
What makes a password strong?
- Length beats everything. Each extra character multiplies the guesses an attacker needs.
- A mix of letters, digits, and symbols helps — but a long passphrase like
correct horse battery stapleis both strong and memorable.
한국어
비밀번호를 강력하게 만드는 방법
- 길이야 최우선이다. 한 글자만 늘려도 공격자가 시도해야 할 경우의 수가 배가된다.
- 문자, 숫자, 기호를 섞는 것이 도움이 되지만,
correct horse battery staple과 같은 긴 패스프레이즈는 강력하면서도 기억하기 쉽다.
English
Build a checker
- Below, write a tiny rule: a password is "strong" only if it is long enough and has a digit.
- Real checkers also reject common passwords like
123456andpassword.
Covers: IGCSE 5.3 (authentication), A-Level 6.1, AP CSP Big Idea 5.
한국어
체크리스트 만들기
- 아래에 작은 규칙을 작성하시오: 비밀번호는 충분히 길고 그리고 숫자를 포함할 때만 '강력'하다고 판단합니다.
- 실제 체크리스트는
123456및password와 같은 일반적인 비밀번호도 거절합니다.
내용: IGCSE 5.3 (인증), A-Level 6.1, AP CSP Big Idea 5.
English
Common mistakes
- Long and unique beats short, complex, but reused.
- Two-factor authentication adds a second, different check.
한국어
흔한 실수
- 짧고 복잡하지만 반복적으로 사용하는 것보다, 길고 고유한 비밀번호가 낫습니다.
- 2중 인증은 두 번째, 서로 다른 검증 단계를 추가합니다.
Write a simple strength checker. A password is strong if it is at least 8 characters AND contains a digit; otherwise weak. Print the right word for the given password. · 간단한 강도 검사를 작성하십시오. 비밀번호가 최소 8글자 AND 숫자를 포함하면 strong이고, 아니면 weak입니다. 주어진 비밀번호에 맞는 단어를 출력하십시오.
Click Run to see the output here. · 출력을 보려면 '실행'을 클릭하세요.
Real checkers also reject common passwords. Improve the rule: if the password is in the common list it is weak no matter what; otherwise apply the old rule (length ≥ 8 AND a digit). Print the verdict. · 실제 검증자는 일반적인 비밀번호도 거절합니다. 규칙을 개선하십시오: 비밀번호가 common 목록에 있으면 어떤 상황에서도 weak이며, 아니면 이전 규칙(길이 ≥ 8 AND 숫자 포함)을 적용하십시오. 판정을 출력하십시오.
Click Run to see the output here. · 출력을 보려면 '실행'을 클릭하세요.