SQL injection · הזרקת SQL
This page needs a recent browser (with SharedArrayBuffer support). Please update Chrome, Edge, Firefox or Safari to the latest version. · עמוד זה דורש דפדפן עדכני (תומך ב-SharedArrayBuffer). אנא עדכן את Chrome, Edge, Firefox או Safari לגרסה העדכנית ביותר.
English
When input becomes a command
- Many apps build a database query by gluing the user's input into a string. That is dangerous.
- If an attacker types SQL as their input, it can become part of the query. This is SQL injection — the most famous web attack.
עברית
כשקלט הופך לפקודה
- רבים מייצרים שאילתות מסד נתונים על ידי הדבקת קלט המשתמש לתוך מחרוזת. זה מסוכן.
- אם מתקיף הקלד SQL כקלט שלו, הוא יכול להפוך לחלק מהשאילתה. זהו הזרקת SQL — ההתקפה הידועה ביותר ברשת.
English
See the attack
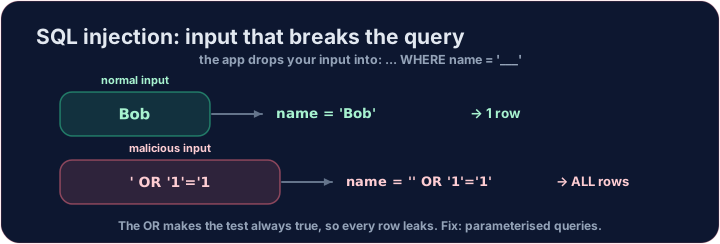
- Imagine a login that checks
... WHERE name = '<whatever you typed>'. - An attacker types
' OR '1'='1as the name. The query becomes:
'1'='1'is always true, so the database returns every user. The login is bypassed. Run it and see.
עברית
לראות את ההתקפה
- דמיינו התחברות שבודקת
... WHERE name = '<whatever you typed>'. - מתקיף הקלד
' OR '1'='1כשם. השאילתה הופכת ל:
SELECT * FROM users WHERE name = '' OR '1'='1';
'1'='1'הוא תמיד נכון, ולכן מסד הנתונים מחזיר כל המשתמשים. ההתחברת נעקפת. הרץ זאת וראה.
English
The fix: parameterised queries
- Never glue user input into SQL. Use parameterised queries (also called prepared statements).
- The database treats the input strictly as a value, never as code — so
' OR '1'='1is just a (failed) name to look up. - Also apply least privilege: the web app's database account should only do what it needs.
עברית
הפתרון: שאילתות פרמטריות
- ** לעולם ** אל תחבר קלט משתמש ל-SQL. השתמש בשאילתות פרמטריות (נקראות גם פקודות מוכנות).
- מסד הנתונים טיפל בקלט בחמרה כערך, לעולם לא כקוד – כך ש
' OR '1'='1הוא רק שם (כשל) לחיפוש. - יישם גם זכויות מינימליות: חשבון מסד הנתונים של האפליקציה ברשת צריך לעשות רק מה שהוא צריך.
English
Your turn
- Below, write a precise, safe query that returns only bob by his
id. That is the spirit of a parameterised lookup.
Covers: A-Level data security; web application security.
עברית
תורך
- למטה, כתוב שאילתה מדויקת ובטוחה שמחזירה רק את bob לפי
id. זהו הרעיון של חיפוש מופרמטר.
מכסה: אבטחת נתונים ברמת A-Level; אבטחת אפליקציות אינטרנט.
English
Common mistakes
- Never build a query by joining raw user input into the text.
- Use parameterised queries so input can never change the query.
עברית
טעויות נפוצות
- לעולם אל תבנה שאילתה על ידי חיבור קלט משתמש גולמי לטקסט.
- השתמש בשאלות מופרמטר כך שקלט לעולם לא ישנה את השאילתה.
First, run the attack and see the damage. The app glued the attacker's input into the query, so the condition became name = '' OR '1'='1'. Complete the query exactly like that and see every user leak out. · תחילה, הרץ את ההתקפה וראה את הנזק. האפליקציה חיברה את קלט המתקיף לשאלה, כך שהתנאי הפך לname = '' OR '1'='1'. השלם את השאלה בדיוק ככה וראה כל המשתמשים דולפים החוצה.
Click Run to see the output here. · לחץ על הרץ כדי לראות את התוצא כאן.
A safe lookup uses a precise condition. Change the query to return only bob's row, by adding WHERE id = 2. · חיפוש בטוח משתמש בתנאי מדויק. שנה את השאלה כדי להחזיר רק את שורת בוב, על ידי הוספת WHERE id = 2.
Click Run to see the output here. · לחץ על הרץ כדי לראות את התוצא כאן.