Hashing and digital signatures · גישוח וחתימות דיגיטליות
Hashing protects integrity
- We hashed passwords for secrecy. Hashing also protects integrity — proving data was not changed.
- Change even one character of the input, and the hash changes completely.
Hashing מגן על שלמות
- השתמשנו ב-Hashing להגנת סודיות passwords. Hashing גם מגן על שלמות — מוכיח שהנתונים לא שונו.
- שינוי אפילו של תווה אחד בקלט, וה-Hashing משתנה לחלוטין.
import hashlib
print(hashlib.sha256(b"hello").hexdigest()[:16])
print(hashlib.sha256(b"hellp").hexdigest()[:16])   # totally different
Checking a download
- Websites publish the hash of a file. After downloading, you hash your copy and compare.
- If the two hashes match, the file arrived intact. If not, it was corrupted or tampered with.
בדיקת הורדה
- אתרי אינטרנט מפרסמים את חותמת (hash) של קובץ. לאחר ההורדה, תחשב את החותמת של העתק שלך והשווה אותה.
- אם שתי החותמות זהות, הקובץ הגיע שלם. אם לא, הוא הושחת או עבר שינוי זדוני.
Digital signatures
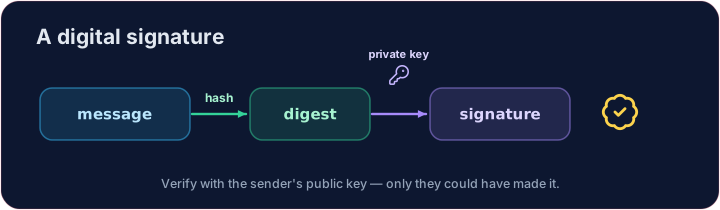
- A digital signature proves who sent something and that it was not changed.
- The sender hashes the message and encrypts that hash with their private key.
- Anyone can check it with the sender's public key — only the real sender could have made it.
חתימות דיגיטליות
- חתימה דיגיטלית מאשרת מי שלח דבר מה וגם כי הוא לא השתנה.
- השולח מחשב את ההודעה ומצפיד את החותמת הזו באמצעות המפתח הפרטי שלו.
- כל אחד יכול לבדוק זאת באמצעות המפתח הציבורי של השולח — רק השולח האמיתי יכל ליצור זאת.
Your turn
- Compare the hashes of an original and a received message.
Truemeans the message is intact.
Covers: A-Level 17.1 (digital certification), 6.2 (integrity).
תורך
- השוו את החותמות של הודעה מקורית ושל הודעה שהתקבלה.
Trueמצביע על כך שההודעה שלמה.
כיסוי: A-Level 17.1 (אישור דיגיטלי), 6.2 (אינטגריות).
Common mistakes
- A hash is one-way — you cannot get the original back from it.
- A digital signature proves who sent a message and that it was not changed.
טעויות נפוצות
- חותמת היא חד-כיוונית — אין אפשרות לקבל בחזרה את המקור ממנה.
- חתימה דיגיטלית מאשרת מי שלח הודעה וכי היא לא השתנתה.
Hashing & signatures · גישוח וחתימות
A hash is one-way and avalanches — perfect for fingerprints. · גשוח הוא חד-כיווני ו-מתפשט — אידיאלי לאצבעות דיגיטליות.
Check whether a received message is unchanged. Hash both original and received with SHA-256 and print whether the two digests are equal (True or False). · בדוק האם הודעה שהתקבלה נותרה ללא שינוי. גשוח את both original ו-received באמצעות SHA-256 והדפס print אם שני הגישוחים זהים (True או False).
Click Run to see the output here. · לחץ על הרץ כדי לראות את התוצא כאן.
This time an attacker edited the message in transit. Hash both versions and print TAMPERED if the digests differ, else OK — one changed character is enough to catch. · פעם זו התוקף ערך את ההודעה במהלך העברתה. גשוח את שתי הגרסאות והדפס TAMPERED אם הגישוחים שונים, אחרת הדפס OK — שינוי של תווית אחת בלבד מספיק כדי להתפוס.
Click Run to see the output here. · לחץ על הרץ כדי לראות את התוצא כאן.