Passwords and authentication · סיסמאות ואישור זהות
Proving who you are
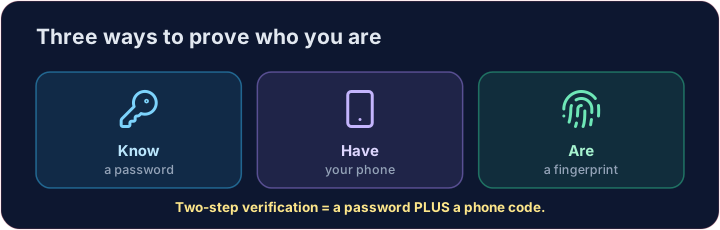
- Authentication means proving you are who you claim to be. There are three classic ways:
- Something you know (a password), something you have (a phone), something you are (a fingerprint).
הוכחת זהותך
- אימות פירונו הוכחה שאתה מי שטוען שאתה. ישנם שלושה דרכים קלאסיות:
- דבר שאתה יודע (סיסמה), דבר שיש לך (טלפון), דבר שאתה (טביעת אצבע).
Stronger logins
- Biometrics — fingerprints or face scans; hard to steal, but not perfect.
- Two-step verification (2FA) — a password plus a one-time code sent to your phone.
- Even if an attacker steals your password, 2FA stops them logging in.
כניסות חזקות יותר
- ביומטריה — טביעות אצבע או סריקת פנים; קשה לגנבה, אך לא מושלמת.
- אימות דו-שלבי (2FA) — סיסמה וגם קוד חד-פעמי שנשלח לטלפון שלך.
- גם אם התוקף גונב את הסיסמה שלך, אימות דו-שלבי (2FA) מונע ממנו להתחבר.
What makes a password strong?
- Length beats everything. Each extra character multiplies the guesses an attacker needs.
- A mix of letters, digits, and symbols helps — but a long passphrase like
correct horse battery stapleis both strong and memorable.
מה הופך סיסמה לחזקה?
- אורך עולה על הכל. כל תווית נוספת מכפילה את מספר הניחושים שנקח לתוקף.
- שילוב של אותיות, ספרות וסימנים עוזר — אך ביטוי ארוך כמו
correct horse battery stapleהוא גם חזק וגם קל לזכירה.
Build a checker
- Below, write a tiny rule: a password is "strong" only if it is long enough and has a digit.
- Real checkers also reject common passwords like
123456andpassword.
Covers: IGCSE 5.3 (authentication), A-Level 6.1, AP CSP Big Idea 5.
בנה בודק
- למטה, כתוב כלל פשוט: סיסמה היא "חזקה" רק אם היא ארוכה מספיק וגם מכילה ספרה.
- בודקים אמיתיים דוחים גם סיסמות נפוצות כמו
123456וpassword.
כיסוי: IGCSE 5.3 (אימות), A-Level 6.1, AP CSP רעיון מרכזי 5.
Common mistakes
- Long and unique beats short, complex, but reused.
- Two-factor authentication adds a second, different check.
טעויות נפוצות
- אורך וייחודיות עולים על קצרה, מורכבת אך משתמשת באותה סיסמה שוב ושוב.
- אימות דו-שלבי מוסיף בדיקה שנייה ושונה.
Write a simple strength checker. A password is strong if it is at least 8 characters AND contains a digit; otherwise weak. Print the right word for the given password. · כתוב בודק עוצמה פשוט. סיסמה היא strong אם יש בה מינימום 8 תווים AND מכילה ספרה; אחרת היא weak. הדפס את המילה הנכונה עבור הסיסמה הנתונה.
Click Run to see the output here. · לחץ על הרץ כדי לראות את התוצא כאן.
Real checkers also reject common passwords. Improve the rule: if the password is in the common list it is weak no matter what; otherwise apply the old rule (length ≥ 8 AND a digit). Print the verdict. · בודקים אמיתיים דוחים גם סיסמאות נפוצות. שיפר את הכלל: אם הסיסמה נמצאת ברשימת common היא weak ללא קשר; אחרת יושם הכלל הקודם (אורך ≥ 8 AND ספרה). הדפס את הפסקה.
Click Run to see the output here. · לחץ על הרץ כדי לראות את התוצא כאן.