SQL injection · injection SQL
When input becomes a command
- Many apps build a database query by gluing the user's input into a string. That is dangerous.
- If an attacker types SQL as their input, it can become part of the query. This is SQL injection — the most famous web attack.
Quand l'entrée devient une commande
- De nombreuses applications construisent une requête de base de données en collant l'entrée utilisateur dans une chaîne. C'est dangereux.
- Si un attaquant tape SQL comme entrée, cela peut faire partie de la requête. C'est l'injection SQL — l'attaque web la plus célèbre.
See the attack
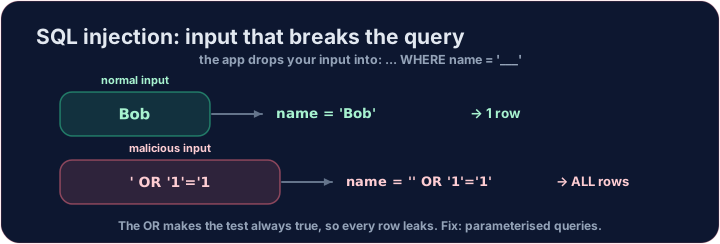
- Imagine a login that checks
... WHERE name = '<whatever you typed>'. - An attacker types
' OR '1'='1as the name. The query becomes:
'1'='1'is always true, so the database returns every user. The login is bypassed. Run it and see.
Voir l'attaque
- Imaginez une connexion qui vérifie
... WHERE name = '<whatever you typed>'. - Un attaquant tape
' OR '1'='1comme nom. La requête devient :
SELECT * FROM users WHERE name = '' OR '1'='1';
'1'='1'est toujours vrai, donc la base de données retourne tous les utilisateurs. La connexion est contournée. Exécutez-le et voyez.
The fix: parameterised queries
- Never glue user input into SQL. Use parameterised queries (also called prepared statements).
- The database treats the input strictly as a value, never as code — so
' OR '1'='1is just a (failed) name to look up. - Also apply least privilege: the web app's database account should only do what it needs.
La correction : requêtes paramétrisées
- Ne jamais coller l'entrée utilisateur dans du SQL. Utilisez des requêtes paramétrisées (aussi appelées instructions préparées).
- La base de données traite l'entrée strictement comme une valeur, jamais comme du code — donc
' OR '1'='1n'est qu'un (mauvais) nom à chercher. - Appliquez aussi le principe de moindre privilège : le compte base de données de l'application web ne devrait faire que ce dont il a besoin.
Your turn
- Below, write a precise, safe query that returns only bob by his
id. That is the spirit of a parameterised lookup.
Covers: A-Level data security; web application security.
À vous
- Ci-dessous, écrivez une requête précise et sûre qui retourne uniquement bob par son
id. C'est l'esprit d'une recherche paramétrisée.
Covers : A-Level sécurité des données ; sécurité des applications web.
Common mistakes
- Never build a query by joining raw user input into the text.
- Use parameterised queries so input can never change the query.
Erreurs courantes
- Ne jamais construire une requête en joignant l'entrée brute utilisateur au texte.
- Utilisez des requêtes paramétrisées pour que l'entrée ne puisse jamais modifier la requête.
First, run the attack and see the damage. The app glued the attacker's input into the query, so the condition became name = '' OR '1'='1'. Complete the query exactly like that and see every user leak out. · D'abord, exécutez l'attaque et voyez les dégâts. L'application a collé l'entrée de l'attaquant dans la requête, donc la condition est devenue name = '' OR '1'='1'. Complétez la requête exactement ainsi et voyez tous les utilisateurs fuir.
Click Run to see the output here. · Cliquez sur Exécuter pour voir le résultat ici.
A safe lookup uses a precise condition. Change the query to return only bob's row, by adding WHERE id = 2. · Une recherche sûre utilise une condition précise. Changez la requête pour retourner uniquement la ligne de bob, en ajoutant WHERE id = 2.
Click Run to see the output here. · Cliquez sur Exécuter pour voir le résultat ici.