Social engineering · الهندسة الاجتماعية
This page needs a recent browser (with SharedArrayBuffer support). Please update Chrome, Edge, Firefox or Safari to the latest version. · تحتاج هذه الصفحة إلى متصفح حديث (يدعم SharedArrayBuffer). يرجى تحديث Chrome أو Edge أو Firefox أو Safari إلى أحدث إصدار.
English
Hacking the human
- The weakest part of any system is often people, not computers.
- Social engineering means tricking a person into giving away secrets or access. No malware needed.
العربية
اختراق الجانب البشري
- الجزء الأضعف في أي نظام هو غالباً الأشخاص، وليس أجهزة الكمبيوتر.
- الهندسة الاجتماعية تعني خداع شخص ما لتسريب أسرار أو وصول. لا حاجة لبرمجيات خبيثة.
English
Phishing and pharming
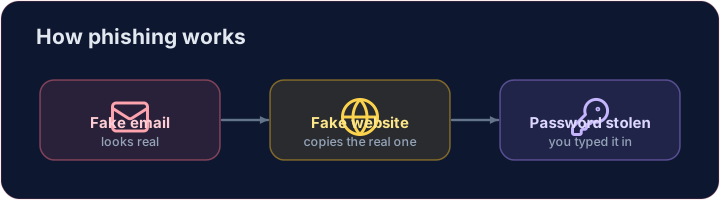
- Phishing — a fake email or message that looks real, asking you to "log in" on a fake site that steals your password.
- Pharming — redirecting you to a fake website even when you typed the correct address.
- Both aim to steal your login details by pretending to be a site you trust.
العربية
التصيد الاحتيالي والتصيد الدوائي
- التصيد الاحتيالي — رسالة بريد إلكتروني مزيفة تبدو حقيقية، تطلب منك "تسجيل الدخول" على موقع مزيف يسرق كلمة المرور.
- التصيد الدوائي — إعادة توجيهك إلى موقع مزيف حتى عندما تكتب العنوان الصحيح.
- كلاهما يهدف لسرعة بيانات تسجيل الدخول عن طريق التظاهر بموقع تثق به.
English
Spotting a phishing message
- Check the sender's address and the link — hover to see where it really goes.
- Watch for urgency ("act now or your account closes!") and spelling mistakes.
- A real bank will never ask for your password by email.
العربية
اكتشاف رسالة تصيد احتيالي
- تحقق من عنوان المرسل والرابط — مرر المؤشر لترى أين يذهب حقاً.
- انتبه إلى الإلحاح ("اتخذ إجراء الآن قبل إغلاق حسابك!") وأخطاء الإملاء.
- لن يطلب بنك حقيقي أبداً كلمة المرور الخاصة بك عبر البريد الإلكتروني.
English
Other tricks
- Shoulder surfing — simply watching you type your PIN.
- Baiting — leaving an infected USB stick for a curious person to plug in.
- The defence is awareness: slow down and check before you click or type.
Covers: IGCSE 5.3 (phishing, pharming, social engineering), AP CSP Big Idea 5.
العربية
حيل أخرى
- التجسس من الكتف — مجرد مراقبة لطريقة كتابة رمزك التعريفي.
- المناغشة — ترك فلاش USB ملوث لأحد الفضوليين لتوصيله.
- الدفاع هو الوعي: ابطئ وتحقق قبل النقر أو الكتابة.
يتناول: IGCSE 5.3 (التصيد الاحتيالي، الصيد الدوائي، الهندسة الاجتماعية)، AP CSP الفكرة الكبرى 5.
English
Now you try
- First build a tiny phishing filter: check the sender's address and where the link really points.
- Then match three more tricks to their names — exactly what the exam asks you to do.
العربية
الآن جرب بنفسك
- أولاً، قم بإنفلتر تصيد احتيالي صغير: تحقق من عنوان المرسل وأين يشير الرابط فعلياً.
- ثم طابق ثلاث حيل أخرى بأسمائها — تماماً كما يطلب منك الامتحان فعله.
English
Common mistakes
- The weakest link is often people, not software.
- Phishing tricks you into giving up secrets — check the sender and the link first.
العربية
أخطاء شائعة
- الحلقة الأضعف غالباً ما تكون البشر، وليس البرمجيات.
- يحيلك التصيد الاحتيالي لتسلي secrets — تحقق من المرسل والرابط أولاً.
Build a tiny phishing filter. The real bank writes from addresses ending @mybank.com and its links start with https://mybank.com. Print phishing if either check fails, otherwise ok. · ابني فلتر تصيد صغير. البنك الحقيقي يرسل من عناوين تنتهي @mybank.com وروابطه تبدأ بـ https://mybank.com. اطبع phishing إذا فشل أي من هذين التحققين، وإلا اطبع ok.
Click Run to see the output here. · اضغط تشغيل لرؤية المخرجات هنا.
Name the trick. Set each variable to shoulder surfing, baiting or pharming. · سمّ الحيلة. اضبط كل متغير على shoulder surfing، baiting أو pharming.
Click Run to see the output here. · اضغط تشغيل لرؤية المخرجات هنا.